Decoding the Handshake
Mastering Transport Layer Security in the Digital Age
Are you ready to unravel the intricate dance of bits and bytes that safeguards our digital world?
269 pages13 chaptersDec 29, 2024Network Programming
About this book
"Decoding the Handshake: Mastering Transport Layer Security in the Digital Age" takes you on an exhilarating exploration of the TLS handshake—the silent guardian of our online communications. This book demystifies the complex world of cryptographic protocols, offering you a front-row seat to the sophisticated mechanisms that protect your data as it travels across the vast digital landscape. You'll dive deep into the heart of TLS, understanding not just the 'what' but the crucial 'why' behind each step of the handshake process. From the fundamentals of key exchange to the nuances of cipher suites, you'll build a robust foundation in modern cryptography. By the time you finish this book, you'll view every secure connection through new eyes, appreciating the elegant ballet of algorithms that occurs in milliseconds every time you connect securely online. Whether you're a curious technologist or a seasoned IT professional, this book will elevate your understanding of network security to new heights. Get ready to see the digital world as you've never seen it before—through the lens of Transport Layer Security.
Table of contents
- IntroductionThe Importance of Transport Layer Security, Overview of the Book's Contents, How to Use This Book EffectivelyRead below
- Chapter 1: Foundations of CryptographyBasic Principles of Cryptography, Symmetric Encryption Algorithms, Asymmetric Encryption and Public Key Infrastructure, Hash Functions and Digital Signatures
- Chapter 2: TLS Protocol OverviewThe Evolution of SSL/TLS, TLS Protocol Architecture, The Four TLS Sub-Protocols, Benefits and Use Cases of TLS
- Chapter 3: The TLS Handshake ProtocolSteps of the TLS Handshake, Client Hello Message, Server Hello and Certificate, Key Exchange and Server Hello Done, Client Key Exchange and Finished
- Chapter 4: Key Exchange ProtocolsDiffie-Hellman Key Exchange, RSA Key Exchange, Elliptic Curve Diffie-Hellman Ephemeral (ECDHE), Comparing Key Exchange Methods
- Chapter 5: Understanding Cipher SuitesComponents of a Cipher Suite, Popular Cipher Suites and Their Strengths, Cipher Suite Selection Process, Future-Proofing Cipher Suite Choices
- Chapter 6: Certificate Validation and TrustX.509 Certificates Explained, Role of Certificate Authorities, Certificate Chain Validation, Certificate Revocation Checking Methods
- Chapter 7: Session Resumption TechniquesSession IDs and Caches, Session Tickets, 0-RTT Resumption in TLS 1.3, Security Considerations in Session Resumption
- Chapter 8: TLS Extensions and EnhancementsServer Name Indication (SNI), Application-Layer Protocol Negotiation (ALPN), OCSP Stapling, Heartbeat Extension
- Chapter 9: TLS 1.3: The Latest EvolutionKey Changes in TLS 1.3, The Streamlined TLS 1.3 Handshake, Privacy Improvements in TLS 1.3, Performance Enhancements in TLS 1.3
- Chapter 10: Implementing TLS in ApplicationsUsing OpenSSL for TLS Implementation, Popular TLS Libraries and SDKs, Configuration Best Practices, Common Implementation Pitfalls and How to Avoid Them
- Chapter 11: Testing and Debugging TLS ConnectionsTools for TLS Connection Testing, Analyzing TLS Traffic with Wireshark, Common Error Scenarios and Troubleshooting, Performance Tuning TLS Connections
- Chapter 12: TLS Attacks and MitigationsProtocol-Level Attacks, Implementation Vulnerabilities, Side-Channel Attacks on TLS, Mitigation Strategies and Best Practices
- Chapter 13: The Future of TLS and Secure CommunicationPost-Quantum Cryptography in TLS, Emerging Secure Communication Protocols, TLS in IoT and Resource-Constrained Environments, Future Research Directions in TLS
- ConclusionKey Takeaways, Continuing Your TLS Education
- Glossary
- Further Reading
Introduction
In the vast digital landscape of the 21st century, where information flows ceaselessly across networks and oceans, the need for secure communication has never been more critical. As you navigate this interconnected world, whether browsing websites, sending emails, or conducting online transactions, a silent guardian works tirelessly to protect your data: Transport Layer Security (TLS). This cryptographic protocol forms the backbone of secure communication on the internet, ensuring that your sensitive information remains confidential and untampered as it traverses the global network infrastructure.
The importance of TLS in our daily digital interactions cannot be overstated. It's the invisible shield that stands between your personal data and those who would seek to intercept or manipulate it. Every time you see that reassuring padlock icon in your browser's address bar, you're witnessing TLS in action, working diligently to establish a secure connection between your device and the server you're communicating with. This process, known as the TLS handshake, is a complex dance of cryptographic algorithms and protocols that occurs in milliseconds, yet its implications for security are profound and far-reaching.
As technology professionals and enthusiasts with an intermediate understanding of cybersecurity and networking protocols, you're already aware of the critical role that secure communication plays in our interconnected world. However, the intricacies of how this security is established, maintained, and evolved often remain shrouded in technical jargon and abstract concepts. This book aims to lift that veil, providing you with a comprehensive understanding of the TLS handshake process and its surrounding ecosystem of cryptographic implementations.
Throughout this journey, you'll delve deep into the heart of secure communication protocols, exploring not just the mechanics of TLS, but also the underlying principles of cryptography that make it possible. You'll gain insights into the evolution of TLS, from its origins as SSL to its current state-of-the-art implementation in TLS 1.3. Along the way, you'll encounter key exchange protocols, cipher suites, certificate validation processes, and much more – all explained with clarity and depth to enhance your professional knowledge and practical skills in implementing robust security measures.
The Importance of Transport Layer Security
Transport Layer Security stands as a cornerstone of modern internet security, providing a crucial layer of protection for data in transit. Its significance extends far beyond simple encryption; TLS ensures the confidentiality, integrity, and authenticity of data exchanged between parties over potentially insecure networks. In an era where cyber threats are increasingly sophisticated and pervasive, understanding and implementing TLS correctly is not just beneficial – it's essential for any organization or individual concerned with protecting sensitive information.
The primary function of TLS is to prevent eavesdropping, tampering, and message forgery. When you connect to a website using HTTPS, for instance, TLS is working behind the scenes to establish a secure channel. This process involves several key security features:
- Encryption: TLS uses robust cryptographic algorithms to scramble data, making it unreadable to anyone who might intercept it during transmission.
- Authentication: Through the use of digital certificates, TLS verifies the identity of the server (and optionally, the client), ensuring you're communicating with the intended party and not an impostor.
- Integrity: TLS employs message authentication codes (MACs) to detect any changes to the data during transmission, preventing man-in-the-middle attacks where an attacker might try to alter the communication.
The importance of TLS becomes even more apparent when considering the vast array of sensitive information transmitted over the internet daily. Financial transactions, personal communications, healthcare data, and corporate secrets all rely on TLS to maintain their confidentiality. Without TLS, the digital economy as we know it would be impossible, as trust in online transactions would be severely compromised.
Moreover, TLS plays a crucial role in compliance with various data protection regulations. Standards such as PCI DSS for payment card information, HIPAA for healthcare data, and GDPR for personal data of EU citizens all require or strongly recommend the use of encryption for data in transit. TLS provides a standardized and widely accepted method for meeting these requirements, helping organizations avoid hefty fines and reputational damage associated with data breaches[1].
The evolving nature of cyber threats necessitates continuous improvement in security protocols. TLS has undergone several iterations since its inception, each addressing vulnerabilities discovered in previous versions and introducing new features to enhance security and performance. Understanding these changes and staying current with the latest TLS developments is crucial for cybersecurity professionals and organizations aiming to maintain robust security postures.
Furthermore, the importance of TLS extends to the realm of search engine optimization (SEO) and user trust. Major search engines like Google have made HTTPS (which relies on TLS) a ranking factor, giving preference to secure websites in search results. This policy not only encourages wider adoption of TLS but also reflects the growing awareness among users about the importance of secure connections. Websites that implement TLS correctly often see improved user trust and engagement, as evidenced by the familiar padlock icon in browser address bars that reassures visitors of a secure connection[2].
As we delve deeper into the intricacies of TLS throughout this book, it's important to keep in mind the broader context of its significance. TLS is not just a technical protocol; it's a fundamental enabler of trust in the digital age. Its proper implementation and understanding are crucial for anyone involved in developing, maintaining, or securing online systems. By mastering TLS, you're not only enhancing your technical skills but also contributing to the overall security and reliability of the internet ecosystem.
In the following chapters, we'll explore every aspect of TLS in detail, from the cryptographic foundations that underpin its security to the latest developments in TLS 1.3. This journey will equip you with the knowledge and insights needed to implement, troubleshoot, and optimize TLS in your own projects and environments. As we progress, you'll gain a deeper appreciation for the elegance and complexity of the TLS handshake process, and how it silently safeguards millions of online interactions every second of every day.
Overview of the Book's Contents
"Decoding the Handshake: Mastering Transport Layer Security in the Digital Age" is structured to provide a comprehensive and in-depth exploration of TLS, starting from the foundational concepts and progressing to advanced topics and future trends. This carefully crafted journey through the world of secure communication protocols is designed to enhance your understanding and practical skills, regardless of your current level of expertise in cybersecurity and networking.
The book is organized into thirteen chapters, each focusing on a crucial aspect of TLS and its implementation. Here's a brief overview of what you can expect from each chapter:
- Foundations of Cryptography: This chapter lays the groundwork for understanding TLS by introducing the basic principles of cryptography. You'll explore symmetric and asymmetric encryption algorithms, hash functions, and digital signatures – the building blocks of secure communication.
- TLS Protocol Overview: Here, you'll get a bird's-eye view of the TLS protocol, its evolution from SSL, and its architecture. This chapter will help you understand the context and structure of TLS before diving into its specific components.
- The TLS Handshake Protocol: This is where we start to unravel the core of TLS. You'll learn about each step of the handshake process in detail, from the initial "hello" messages to the final key establishment.
- Key Exchange Protocols: Delving deeper, this chapter explores various key exchange methods used in TLS, including Diffie-Hellman, RSA, and Elliptic Curve Diffie-Hellman Ephemeral (ECDHE). You'll understand the strengths and use cases of each method.
- Understanding Cipher Suites: Cipher suites are crucial for determining the security parameters of a TLS connection. This chapter will help you navigate the complex world of cipher suites, their components, and selection processes.
As we progress through the book, we'll tackle more advanced topics:
- Certificate Validation and Trust: You'll learn about X.509 certificates, certificate authorities, and the intricate process of validating certificate chains to establish trust in TLS connections.
- Session Resumption Techniques: This chapter explores methods for optimizing TLS performance through session resumption, including session IDs, session tickets, and the new 0-RTT resumption in TLS 1.3.
- TLS Extensions and Enhancements: Here, you'll discover various extensions that add functionality to TLS, such as Server Name Indication (SNI) and Application-Layer Protocol Negotiation (ALPN).
- TLS 1.3: The Latest Evolution: This chapter focuses on the most recent version of TLS, highlighting its improvements in security, privacy, and performance over previous versions.
- Implementing TLS in Applications: Moving from theory to practice, you'll learn how to implement TLS in real-world applications using popular libraries and SDKs, along with best practices and common pitfalls to avoid.
The final chapters of the book address practical aspects and future considerations:
- Testing and Debugging TLS Connections: You'll gain hands-on experience with tools and techniques for testing, analyzing, and troubleshooting TLS connections, essential skills for any cybersecurity professional.
- TLS Attacks and Mitigations: This chapter explores various attacks against TLS, from protocol-level vulnerabilities to implementation flaws and side-channel attacks. You'll learn about mitigation strategies to protect against these threats.
- The Future of TLS and Secure Communication: Finally, we'll look ahead to emerging trends in secure communication, including post-quantum cryptography, challenges in IoT environments, and potential future developments in TLS.
Throughout the book, you'll find practical examples, code snippets, and real-world case studies that illustrate the concepts being discussed. These practical elements are designed to bridge the gap between theory and application, helping you to apply your newfound knowledge in real-world scenarios.
Each chapter builds upon the knowledge gained in previous sections, creating a comprehensive understanding of TLS. However, the chapters are also designed to be relatively self-contained, allowing you to focus on specific areas of interest or to use the book as a reference guide for particular topics.
By the end of this book, you'll have gained a deep understanding of TLS, from its cryptographic foundations to its latest implementations. You'll be equipped with the knowledge to implement TLS securely in your own projects, troubleshoot TLS-related issues, and make informed decisions about secure communication protocols in various contexts.
This comprehensive overview of TLS is not just about understanding a protocol; it's about empowering you to be at the forefront of secure communication in the digital age. As you progress through the chapters, you'll develop a nuanced understanding of the trade-offs between security, performance, and compatibility that are inherent in TLS implementations. This knowledge will prove invaluable whether you're developing secure applications, managing network infrastructure, or advising on cybersecurity strategies.
How to Use This Book Effectively
To get the most out of "Decoding the Handshake: Mastering Transport Layer Security in the Digital Age," it's important to approach the material with a strategy that aligns with your learning style and professional goals. This book is designed to be both a comprehensive guide for those new to the intricacies of TLS and a detailed reference for experienced professionals. Here are some suggestions on how to use this book effectively:
1. Sequential Reading: If you're new to TLS or looking to build a comprehensive understanding from the ground up, it's recommended to read the book sequentially. The chapters are arranged to build upon each other, starting with foundational concepts and progressing to more advanced topics. This approach will give you a structured learning path, ensuring that you have the necessary background knowledge before tackling more complex subjects.
2. Topic-Based Exploration: For readers already familiar with certain aspects of TLS, or those looking to focus on specific areas, each chapter is designed to be relatively self-contained. You can use the table of contents to identify chapters or sections that are most relevant to your current needs or interests. For instance, if you're particularly interested in the latest developments, you might want to jump to the chapter on TLS 1.3, while those focused on implementation might prioritize the chapters on implementing TLS in applications and testing and debugging TLS connections.
3. Hands-On Practice: Throughout the book, you'll find code examples, configuration snippets, and practical exercises. To truly internalize the concepts, it's highly recommended that you try these out in a safe, controlled environment. Set up a test environment on your local machine or in a sandbox where you can experiment with TLS configurations, run handshake simulations, and test various scenarios discussed in the book. Practical experience is invaluable in solidifying your understanding of TLS.
4. Note-Taking and Summarization: As you read, make notes on key concepts, important terms, and any questions that arise. After each chapter, try summarizing the main points in your own words. This active engagement with the material will help reinforce your learning and make it easier to recall information later. Consider creating your own quick-reference sheets for topics like cipher suite components or steps in the TLS handshake process.
5. Utilize Additional Resources: While this book aims to be comprehensive, the field of cryptography and network security is vast. Make use of the "Further Reading" section at the end of the book to explore topics that particularly interest you in more depth. Additionally, stay current with the latest developments in TLS by following reputable cybersecurity blogs, attending conferences, or participating in online forums dedicated to network security.
6. Apply to Real-World Scenarios: As you progress through the book, constantly think about how the concepts apply to your work or projects. If you're involved in web development, consider how you might implement or improve TLS in your applications. If you're in network administration, think about how you can use this knowledge to enhance your organization's security posture. The true value of this knowledge comes from its practical application.
7. Revisit and Review: Don't hesitate to revisit chapters or sections as needed. TLS is a complex subject, and it's normal to need multiple passes to fully grasp certain concepts. Use the book as a reference guide when you encounter TLS-related issues or questions in your work.
8. Engage with Code Examples: For the programming examples provided, try to run them on your own system. Modify the code, experiment with different parameters, and observe the results. This hands-on approach will deepen your understanding of how TLS works in practice.
9. Use Diagrams and Illustrations: Pay special attention to the diagrams and illustrations throughout the book. These visual aids are designed to help clarify complex processes and relationships within TLS. Try recreating these diagrams from memory as a way to test and reinforce your understanding.
10. Group Study and Discussion: If possible, engage in discussions about the material with colleagues or in online forums. Explaining concepts to others and hearing different perspectives can significantly enhance your understanding and retention of the material.
11. Practical Projects: Consider undertaking a project that involves implementing or analyzing TLS. This could be setting up a secure web server, conducting a security audit of existing TLS implementations, or developing a tool to analyze TLS handshakes. Practical application of the knowledge gained from this book will solidify your understanding and provide valuable hands-on experience.
12. Stay Updated: The field of cryptography and network security is constantly evolving. Use this book as a foundation, but make an effort to stay informed about new developments, vulnerabilities, and best practices in TLS. Consider setting up alerts for TLS-related news or following key figures and organizations in the field on social media.
Remember, the goal of this book is not just to impart information, but to empower you with a deep understanding of TLS that you can apply in your professional life. Whether you're securing web applications, managing network infrastructure, or developing security policies, the knowledge gained from this book should serve as a powerful tool in your cybersecurity arsenal.
As you embark on this journey through the intricacies of TLS, approach the material with curiosity and patience. The concepts you'll encounter are sophisticated, but with diligent study and practice, you'll gain a mastery of TLS that will serve you well in navigating the complex landscape of modern cybersecurity. Embrace the challenges, celebrate your progress, and remember that every step forward in understanding TLS is a step toward a more secure digital world.
This is the end of the free sample. The full book has 13 chapters.
Want this book written for you?
Tell us your goals and background, and get your own version of this book, tailored by AI to you.


Benefits of AI-tailored books
- Read one book, not ten:
- all the Network Programming knowledge you need, gathered into a single book.
- Save days of learning:
- tell us your goals, choose your topics, and the whole book is built around them.
- Learn effortlessly:
- Network Programming book written for your specific background and expertise.
- Understand at a glance:
- includes charts, tables, timelines, checklists, decision trees, and more.
- Stay current:
- written the day you order it, not years ago.
- Trust what you read:
- every book is checked for accuracy, with real research when your subject needs it.
Create your unique book in 3 steps
- 1. Select your focus
Select the focus of your Network Programming book and share your background
- 2. Personalize your book
Specify your goals and choose sub-topics to include
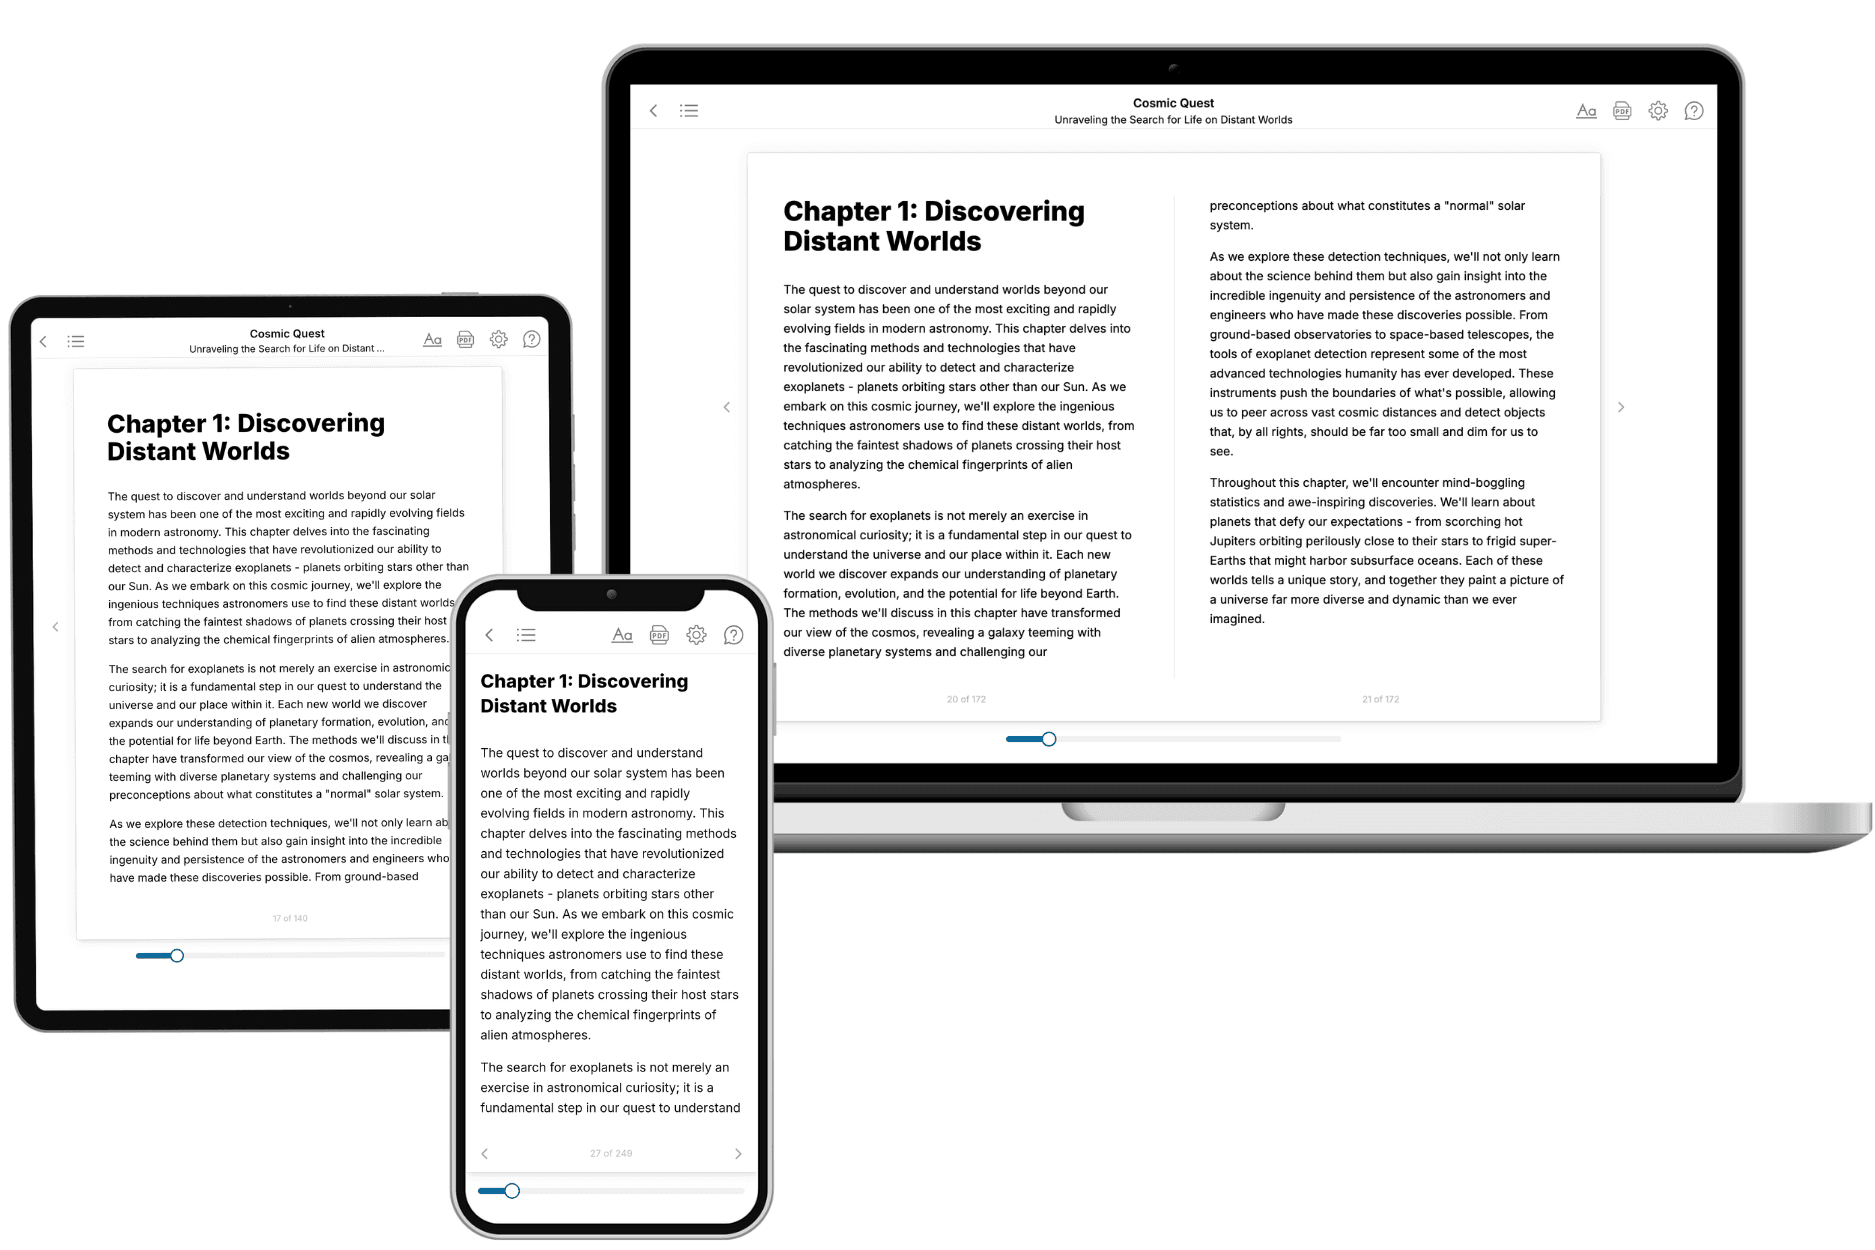
- 3. Get your tailored book
Your book is ready in 10 minutes. Read it online, download as EPUB or PDF, or send to Kindle.
Frequently asked questions
- What is TailoredRead?
TailoredRead creates complete, full-length nonfiction ebooks, written specifically for you. Tell us what you want to learn and why, and TailoredRead writes you a complete ebook on it, with charts, tables, and diagrams throughout. Read it online, on Kindle, or on any e-reader, or download it as a PDF or EPUB. Every book is written fresh the day you order it.
- How is the book tailored to me?
Before anything is written, you answer a few short questions about your goals, your background, and the topics you care about. Your book is then planned around your answers: written at your level, focused on your goals, and covering the topics you chose, instead of the one-size-fits-all book a store sells everyone.
- Will it read like generic AI content?
No. Your book isn't a chat transcript: it's planned chapter by chapter before a single word is written, told in a clear book voice, and explains ideas visually with charts, tables, and diagrams. After writing, every book goes through an editorial pass that polishes chapters so the book reads consistent from start to finish. Judge for yourself: browse thousands of sample books on our Explore Books page.
- How accurate is the content?
Our AI first checks whether your subject needs live research. Niche and fast-moving subjects are researched before writing, and the book plan and chapters are grounded in what it finds. After writing, every book goes through a quality pass that checks its facts and consistency, and researched books list their sources in a Notes section at the back.
- How long is the book?
You choose the length: Comprehensive (250-300 pages), Detailed (150-200 pages), Essential (70-100 pages), or Short (30-50 pages).
- Does the book include visuals?
Yes. Every book includes charts, tables, and diagrams: timelines, checklists, step-by-step guides, decision trees, comparison tables, matrices, and bar charts. A typical book includes dozens of these visual elements.
- Can I read it on Kindle? What formats can I download?
Yes. Every book can be read in our online reader or downloaded as a PDF or EPUB. The EPUB can be opened with Kindle, Apple Books, Kobo, and any e-reader. The Commercial and Author licenses also include an editable Word (DOCX) and Markdown download.
- How much does it cost?
About the price of a regular ebook. The exact price depends on your book's length and complexity, from $2 for the shortest books to $35 for the most comprehensive, and it's shown when you review your book, before you commit to anything. Each book is a one-time purchase, yours to keep, no subscription. Licenses that let you share, teach, or publish your book range from $35.99 to $49.99.
- Can I preview the book before purchasing?
Before you pay, you'll see what your book will cover: the title, a detailed description, the estimated length, and the complete chapter-by-chapter table of contents, so you know what you're getting before you decide. The full text itself is written after you purchase.
- How long does it take to create a book?
About 10 minutes. You can start reading the opening chapters while the rest is still being written.