DES Encryption Demystified
Understanding the Data Encryption Standard and Its Role in Modern Cryptography
What makes a 56-bit encryption key fundamentally different from a 128-bit one, and why does that difference matter for your data security?
222 pages10 chaptersDec 6, 2025Cryptography Algorithms
About this book
This book cuts through the complexity of DES encryption to reveal how one of history's most influential ciphers actually works. You'll explore the elegant mathematics behind the Data Encryption Standard, from its Feistel network architecture to the intricate substitution and permutation operations that transform plaintext into ciphertext. Whether you're a security professional, developer, or curious technologist, you'll gain practical insights into why DES shaped modern cryptography and why understanding its limitations is essential for implementing secure systems today. This guide balances technical depth with accessibility, using clear explanations and real-world context to help you grasp both the mechanics and the implications of this foundational encryption algorithm.
Table of contents
- IntroductionWhy DES Matters Today, Cryptography Foundations You Need to Know, Your Roadmap Through This BookRead below
- Chapter 1: The History and Context of DESCryptography Before DES, How DES Was Developed and Adopted, DES's Impact on Modern Cryptography
- Chapter 2: Symmetric Encryption and Block CiphersUnderstanding Symmetric Encryption, Block Cipher Principles and Design, Where DES Fits in the Cipher Landscape
- Chapter 3: DES Architecture and the Feistel NetworkThe Feistel Network Explained, The 16 Rounds of DES Processing, Key Schedule and Key Generation
- Chapter 4: Substitution and Permutation OperationsS-Boxes: The Heart of DES Nonlinearity, P-Boxes and Permutation Functions, Initial and Final Permutations
- Chapter 5: The DES Encryption Process Step-by-StepWalking Through a Complete Encryption, How Decryption Works in DES, Practical Example with Real Data
- Chapter 6: DES Security Analysis and VulnerabilitiesThe 56-Bit Key Size Problem, Brute-Force Attacks Against DES, Differential and Linear Cryptanalysis
- Chapter 7: Triple DES and Enhanced SecurityHow Triple DES Extends DES Security, Triple DES Implementation Modes, Performance and Practical Considerations
- Chapter 8: DES Operating Modes and ApplicationsElectronic Codebook (ECB) Mode, CBC, CTR, and Other Operating Modes, Real-World Applications of DES
- Chapter 9: The Transition to AES and Modern StandardsWhy AES Replaced DES, Comparing AES and DES Architecture, Migrating from DES to Modern Encryption
- Chapter 10: Implementing DES: Practical ConsiderationsSoftware Implementation Approaches, Hardware Acceleration and Optimization, Supporting DES in Legacy Systems
- ConclusionKey Takeaways and Lessons Learned, The Future of Encryption Standards
- Glossary
- Further Reading and Resources
Introduction
In 1977, the United States government did something unprecedented: it published the complete specifications of a cryptographic algorithm designed to protect sensitive information. This algorithm, the Data Encryption Standard, would go on to become the most widely studied cipher in history. For nearly two decades, DES protected everything from financial transactions to government communications, establishing the foundation for how we think about encryption today. Yet by the late 1990s, security researchers demonstrated they could break DES encryption in less than 24 hours using specialized hardware. This dramatic rise and fall tells us something crucial about cryptography: understanding how encryption works—and how it fails—is essential for anyone working with secure systems.
DES represents a pivotal moment when cryptography transitioned from a secretive art practiced by governments and militaries to a public science subject to rigorous academic scrutiny. Before DES, encryption algorithms were closely guarded secrets, their security dependent on obscurity rather than mathematical rigor. The publication of DES changed everything. Cryptographers worldwide could examine its structure, test its weaknesses, and develop new attack methods. This transparency paradoxically made encryption stronger, not weaker. The lessons learned from analyzing DES directly influenced the design of every modern cipher, including the Advanced Encryption Standard that replaced it. When you understand DES, you gain insight into the fundamental principles that govern all symmetric encryption.
This book takes you inside the machinery of DES encryption, revealing how a seemingly simple process of substitution and permutation creates security strong enough to protect data for years—and why that's no longer sufficient today. You'll explore the elegant Feistel network architecture that makes DES both efficient and reversible, examine the mysterious S-boxes that provide nonlinearity, and understand why a 56-bit key seemed adequate in 1977 but became fatally inadequate by 1998. More importantly, you'll discover how the vulnerabilities discovered in DES shaped modern cryptographic design principles. Whether you're implementing security systems, evaluating encryption standards, or simply curious about how digital security works, understanding DES provides essential context for making informed decisions about protecting data in contemporary environments.
Why DES Matters Today
You might reasonably ask why you should invest time learning about an encryption algorithm that security experts declared obsolete more than two decades ago. The answer lies in understanding that DES isn't just a historical artifact—it's a living case study in cryptographic design, security analysis, and the evolution of computational threats. Every modern encryption standard exists in response to lessons learned from DES. When the National Institute of Standards and Technology designed the competition that produced AES, they explicitly addressed DES's limitations: insufficient key length, vulnerability to differential cryptanalysis, and performance constraints. Understanding what made DES vulnerable helps you evaluate whether contemporary encryption methods adequately address similar threats.
DES remains surprisingly prevalent in legacy systems that continue operating in critical infrastructure, financial networks, and industrial control systems. A 2019 security audit of payment processing systems found that approximately 15% still relied on DES or Triple DES for certain operations[1]. If you work in security, you'll likely encounter DES implementations that need evaluation, migration planning, or compatibility support. Knowing how DES works—and more importantly, how it fails—enables you to assess risk accurately and develop appropriate mitigation strategies. You can't simply declare that all DES usage must cease immediately; you need to understand the specific vulnerabilities, evaluate the threat model for each use case, and prioritize migration efforts based on actual risk.
Beyond practical considerations, DES serves as an ideal educational foundation for understanding symmetric encryption. Its structure is complex enough to demonstrate real cryptographic principles but simple enough to comprehend without advanced mathematics. The Feistel network architecture used in DES appears in numerous other ciphers, including Blowfish, Twofish, and Camellia. The concept of S-boxes providing nonlinear transformation is central to AES. The key schedule mechanism that generates round keys from a master key is a universal feature of block ciphers. By thoroughly understanding DES, you build mental models that transfer directly to analyzing more complex modern algorithms. Think of DES as the equivalent of studying internal combustion engines: even though electric vehicles represent the future, understanding how traditional engines work provides insight into fundamental principles of energy conversion and mechanical design.
The security vulnerabilities discovered in DES also provide invaluable lessons about cryptographic assumptions and the importance of security margins. When DES was designed, its creators believed that 56-bit keys provided adequate security because exhaustively testing all possible keys would require centuries of computation. They were correct—for 1977 technology. What they underestimated was the exponential growth in computational power described by Moore's Law. By 1998, the Electronic Frontier Foundation built a specialized DES-cracking machine called Deep Crack for less than $250,000 that could break DES encryption in days[2]. This demonstrates a crucial principle: cryptographic security must account not just for current computational capabilities but for reasonable projections of future capabilities. Modern standards like AES use 128-bit, 192-bit, or 256-bit keys specifically to provide security margins that remain adequate even with dramatic increases in computing power.
DES also illustrates the tension between theoretical security and practical cryptanalysis. For years, DES was considered theoretically secure against all attacks except brute force. Then in 1990, Eli Biham and Adi Shamir published their work on differential cryptanalysis, demonstrating that DES had structural weaknesses that could be exploited[3]. Remarkably, evidence later emerged that DES's designers at IBM knew about differential cryptanalysis in the 1970s and had specifically strengthened the S-boxes against it—but kept this knowledge classified. This reveals important lessons about the value of public cryptographic research and the dangers of security through obscurity. Modern cipher design embraces transparency, with algorithms subjected to years of public analysis before adoption as standards.
Understanding DES's role in the broader cryptographic ecosystem helps you appreciate how encryption standards evolve. DES didn't simply disappear when its weaknesses became apparent; instead, Triple DES emerged as a transitional solution that extended DES's useful life by applying the algorithm three times with different keys. This pragmatic approach acknowledged the reality that organizations had invested heavily in DES implementations and couldn't instantly migrate to new standards. Triple DES remains approved for certain applications even today, though it's being phased out in favor of AES. This pattern of gradual transition, backward compatibility, and coexistence of old and new standards characterizes real-world cryptography. When you understand this context, you're better equipped to navigate the complex landscape of encryption standards, compliance requirements, and security recommendations that govern contemporary systems.
Finally, DES matters because it represents a democratization of cryptography that fundamentally changed information security. Before DES, strong encryption was primarily available to governments and large corporations with the resources to develop proprietary systems. The publication of DES as a federal standard meant that any organization could implement strong encryption using publicly documented methods. This accessibility sparked the development of the commercial encryption industry and enabled the secure electronic commerce that underpins the modern digital economy. The debates surrounding DES—about key length, government backdoors, and export restrictions—foreshadowed contemporary discussions about encryption policy, privacy rights, and the balance between security and law enforcement access. Understanding DES's history provides essential context for engaging with these ongoing policy debates.
Cryptography Foundations You Need to Know
Before diving into DES's technical details, you need to understand several foundational cryptographic concepts that frame how encryption works. At its core, cryptography addresses a fundamental problem: how can two parties communicate securely over an insecure channel? Imagine you want to send a confidential message to a colleague, but you know that adversaries might intercept it. Encryption transforms your original message (called plaintext) into an unintelligible form (called ciphertext) using a mathematical algorithm and a secret key. Only someone possessing the correct key can reverse this transformation and recover the original plaintext. This process seems simple in concept but requires careful mathematical design to resist sophisticated attacks.
DES belongs to a category called symmetric encryption, where the same key is used for both encryption and decryption. This contrasts with asymmetric encryption (like RSA), where different but mathematically related keys handle encryption and decryption. Symmetric encryption offers significant advantages in speed and efficiency, making it ideal for encrypting large amounts of data. However, it introduces a critical challenge: how do the communicating parties securely share the secret key? If an adversary intercepts the key, all encrypted communications become vulnerable. In practice, modern systems often use asymmetric encryption to securely exchange symmetric keys, then use symmetric encryption for the actual data transfer. Understanding this hybrid approach helps you appreciate why both encryption types remain important despite their different characteristics.
DES specifically implements a block cipher, which encrypts data in fixed-size chunks called blocks. DES processes 64-bit blocks, meaning it takes 64 bits of plaintext as input and produces 64 bits of ciphertext as output. This block-oriented approach contrasts with stream ciphers, which encrypt data one bit or byte at a time. Block ciphers offer certain security advantages and work well for encrypting stored data, while stream ciphers excel at encrypting continuous data streams like network traffic. When you encrypt a message longer than 64 bits with DES, you must divide it into multiple blocks and apply the encryption algorithm to each block. The method you use to handle these multiple blocks—called the mode of operation—significantly affects security, as you'll discover in later chapters.
The concept of confusion and diffusion, introduced by Claude Shannon in 1949, provides the theoretical foundation for understanding how DES achieves security. Confusion means that the relationship between the ciphertext and the key should be as complex as possible, making it difficult for an attacker to deduce the key even if they have many plaintext-ciphertext pairs. DES achieves confusion primarily through its substitution operations (S-boxes), which perform nonlinear transformations that obscure the relationship between input and output. Diffusion means that changing a single bit of plaintext should affect many bits of ciphertext, and changing a single bit of the key should affect many bits of ciphertext. DES achieves diffusion through its permutation operations (P-boxes) and its iterative round structure, which spreads the influence of each input bit throughout the output.
Understanding key space is essential for evaluating encryption strength. The key space is the total number of possible keys an encryption algorithm can use. DES uses a 56-bit key, which means there are 256 possible keys—approximately 72 quadrillion. This sounds like an enormous number, but modern computers can test billions of keys per second. An attacker attempting a brute-force attack simply tries every possible key until finding the correct one. The security of any encryption algorithm ultimately depends on whether the key space is large enough that brute-force attacks require impractical amounts of time and resources. In 1977, testing 72 quadrillion keys was infeasible; by 1998, it became achievable in days. This illustrates why key length is a critical security parameter and why modern standards use much larger keys.
The principle of Kerckhoffs's principle states that a cryptographic system should remain secure even if everything about the system, except the key, is public knowledge. This principle, formulated in 1883, directly contradicts the intuitive notion that keeping your encryption algorithm secret provides additional security. In practice, assuming your algorithm will remain secret is dangerous because reverse engineering, insider leaks, or independent discovery can expose it. DES exemplifies Kerckhoffs's principle: its complete specifications are public, yet it provided strong security for years because the key remained secret. Modern cryptography embraces this principle, with algorithms subjected to extensive public analysis before adoption. When evaluating encryption systems, you should be immediately suspicious of any proprietary algorithm whose details are kept secret—history shows that such systems almost invariably contain serious flaws.
Finally, you need to understand the concept of cryptanalysis—the science of breaking encryption without knowing the key. Cryptanalysis encompasses various attack methods beyond simple brute force:
- Known-plaintext attacks: The attacker has access to some plaintext-ciphertext pairs and tries to deduce the key or decrypt other ciphertexts
- Chosen-plaintext attacks: The attacker can choose specific plaintexts to encrypt and analyze the resulting ciphertexts
- Chosen-ciphertext attacks: The attacker can choose specific ciphertexts to decrypt and analyze the resulting plaintexts
- Differential cryptanalysis: The attacker analyzes how differences in plaintext pairs affect differences in ciphertext pairs
- Linear cryptanalysis: The attacker exploits linear approximations of the cipher's nonlinear operations
Your Roadmap Through This Book
This book takes you on a structured journey from DES's historical context through its technical architecture to its security implications and legacy. Each chapter builds on previous concepts, gradually deepening your understanding of both DES specifically and symmetric encryption generally. The progression is designed to balance theoretical understanding with practical application, ensuring you can both comprehend the mathematics and evaluate real-world security implications. You don't need to read the chapters in strict sequence, but the book is structured to introduce concepts in logical order, with later chapters assuming familiarity with earlier material.
Chapter 1 establishes the historical context by exploring cryptography before DES, the political and technical circumstances that led to its development, and its profound impact on modern cryptography. Understanding this history helps you appreciate why DES was designed the way it was and why certain design decisions that seem questionable today made sense in the 1970s. You'll discover how the National Security Agency's involvement in DES's design sparked controversy and conspiracy theories, some of which were later validated when classified documents revealed that the NSA had indeed influenced certain design choices—but primarily to strengthen the algorithm against attacks that weren't publicly known at the time. This chapter also examines how DES's adoption as a federal standard catalyzed the commercial encryption industry and sparked academic cryptographic research.
Chapters 2 and 3 establish the technical foundation by explaining symmetric encryption principles, block cipher design, and the Feistel network architecture that forms DES's structural backbone. You'll learn why the Feistel network is particularly elegant: it allows the same algorithm to perform both encryption and decryption simply by reversing the order of round keys, eliminating the need for separate encryption and decryption implementations. These chapters introduce key concepts like round functions, key schedules, and the balance between security and performance. You'll understand why DES uses 16 rounds of processing and how each round contributes to the overall security. The explanations include diagrams and step-by-step walkthroughs that make the abstract mathematics concrete and comprehensible.
Chapter 4 dives deep into the substitution and permutation operations that give DES its security properties. The S-boxes (substitution boxes) are particularly fascinating: these small lookup tables provide the nonlinearity essential for security, and their design remains somewhat mysterious even today. You'll explore how S-boxes transform 6-bit inputs into 4-bit outputs in ways that resist linear and differential cryptanalysis. The P-boxes (permutation boxes) complement the S-boxes by spreading the influence of each bit throughout the data block, ensuring that small changes in input produce large changes in output. This chapter reveals how these seemingly simple operations combine to create complex, secure transformations that have resisted decades of cryptanalytic scrutiny.
Chapter 5 provides a complete walkthrough of the DES encryption process, taking you step-by-step through encrypting a 64-bit plaintext block. You'll follow the data through the initial permutation, all 16 rounds of Feistel processing, and the final permutation. This chapter includes a practical example with actual binary data, showing exactly how each operation transforms the bits. You'll also learn how decryption works—which is remarkably similar to encryption due to the Feistel network's reversible structure. By the end of this chapter, you'll be able to trace the encryption process yourself and understand exactly what happens to your data when DES encrypts it. This detailed understanding is essential for evaluating security and troubleshooting implementation issues.
Chapters 6 and 7 shift focus to security analysis, examining DES's vulnerabilities and the Triple DES solution that extended its useful life. You'll learn why the 56-bit key size became DES's fatal weakness and how the Deep Crack machine demonstrated that brute-force attacks were practical. The chapters explain differential and linear cryptanalysis in accessible terms, showing how these sophisticated attacks exploit subtle statistical patterns in the cipher's behavior. You'll discover why Triple DES, despite being slower than single DES, provides dramatically improved security by effectively using 112-bit or 168-bit keys. These chapters also address practical questions: When is Triple DES still acceptable? What threat models does it adequately address? When must you migrate to AES?
Chapters 8 and 9 explore DES in practical contexts, covering operating modes that enable encrypting messages longer than 64 bits and examining real-world applications. You'll learn why Electronic Codebook (ECB) mode is dangerously insecure for most applications, while Cipher Block Chaining (CBC) and Counter (CTR) modes provide better security properties. The transition to AES receives detailed attention, with side-by-side comparisons showing how AES addresses DES's limitations through larger block sizes, longer keys, and different structural approaches. You'll gain practical guidance for migrating legacy systems from DES to modern encryption, including strategies for maintaining backward compatibility during transition periods.
Chapter 10 addresses implementation considerations, covering both software and hardware approaches to DES encryption. You'll learn about optimization techniques, performance trade-offs, and the challenges of supporting DES in legacy systems that can't easily migrate to modern standards. This chapter provides practical advice for security professionals who must evaluate existing DES implementations, plan migration strategies, or maintain systems where DES remains in use. The conclusion synthesizes key lessons from DES's history and technical analysis, extracting principles applicable to evaluating any encryption system. You'll finish with a clear understanding of not just how DES works, but how to think critically about cryptographic security in general.
Throughout the book, you'll find concrete examples, practical scenarios, and real-world case studies that illustrate abstract concepts. The goal is not just to teach you about DES, but to develop your ability to analyze and evaluate cryptographic systems critically. By understanding how DES was designed, how it was broken, and how it influenced modern encryption, you'll build a foundation for making informed security decisions in your own work. Whether you're implementing encryption, auditing security systems, or simply seeking to understand how digital security works, this book provides the knowledge you need to engage confidently with symmetric encryption in all its forms.
Notes
Introduction
- 1. Payment Card Industry Security Standards Council, PCI DSS Cryptographic Algorithm Usage Report, 2019
- 2. Electronic Frontier Foundation, Cracking DES: Secrets of Encryption Research, Wiretap Politics & Chip Design, 1998
- 3. E. Biham and A. Shamir, "Differential Cryptanalysis of DES-like Cryptosystems," Journal of Cryptology, 1991
This is the end of the free sample. The full book has 10 chapters.
Want this book written for you?
Tell us your goals and background, and get your own version of this book, tailored by AI to you.


Benefits of AI-tailored books
- Read one book, not ten:
- all the Cryptography Algorithms knowledge you need, gathered into a single book.
- Save days of learning:
- tell us your goals, choose your topics, and the whole book is built around them.
- Learn effortlessly:
- Cryptography Algorithms book written for your specific background and expertise.
- Understand at a glance:
- includes charts, tables, timelines, checklists, decision trees, and more.
- Stay current:
- written the day you order it, not years ago.
- Trust what you read:
- every book is checked for accuracy, with real research when your subject needs it.
Create your unique book in 3 steps
- 1. Select your focus
Select the focus of your Cryptography Algorithms book and share your background
- 2. Personalize your book
Specify your goals and choose sub-topics to include
- 3. Get your tailored book
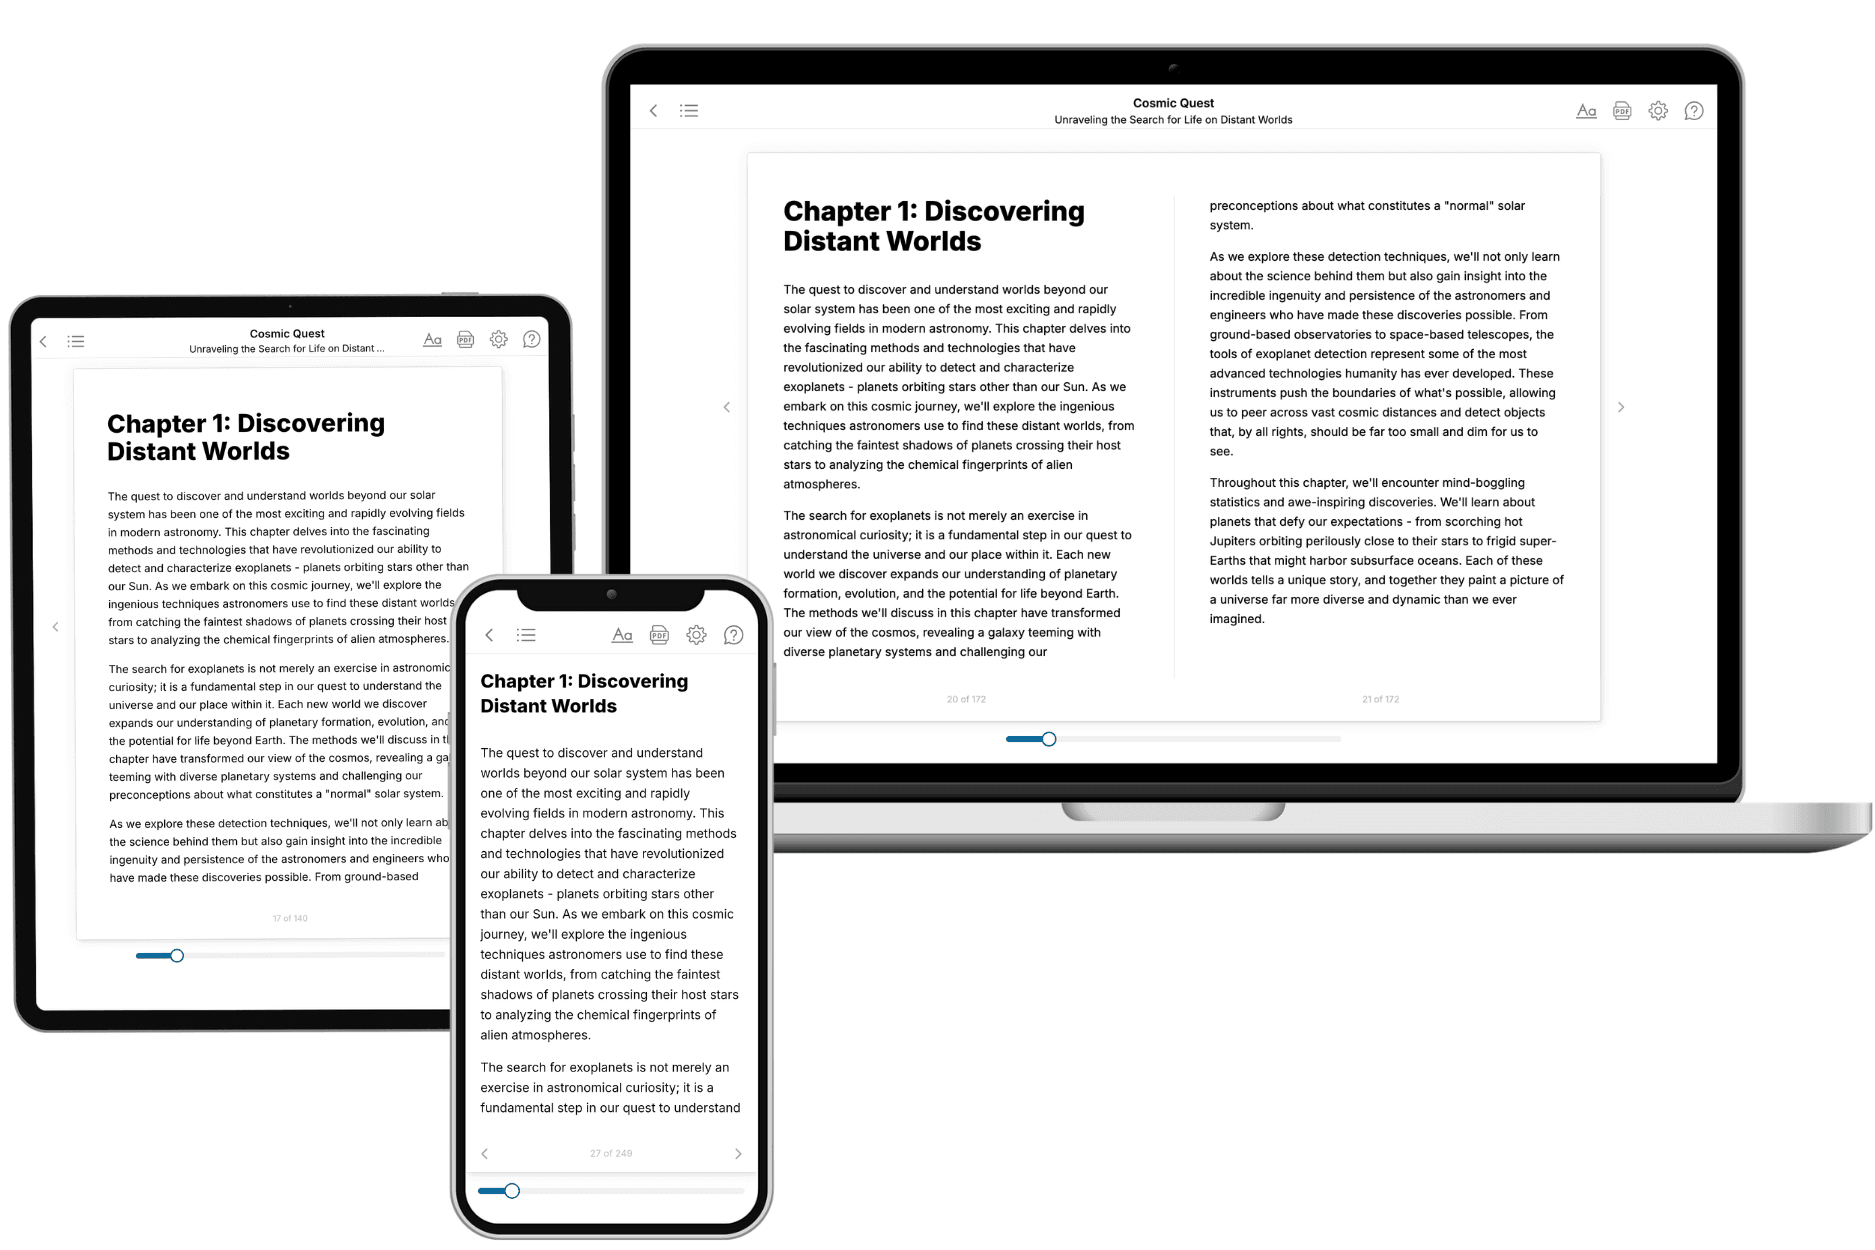
Your book is ready in 10 minutes. Read it online, download as EPUB or PDF, or send to Kindle.
Frequently asked questions
- What is TailoredRead?
TailoredRead creates complete, full-length nonfiction ebooks, written specifically for you. Tell us what you want to learn and why, and TailoredRead writes you a complete ebook on it, with charts, tables, and diagrams throughout. Read it online, on Kindle, or on any e-reader, or download it as a PDF or EPUB. Every book is written fresh the day you order it.
- How is the book tailored to me?
Before anything is written, you answer a few short questions about your goals, your background, and the topics you care about. Your book is then planned around your answers: written at your level, focused on your goals, and covering the topics you chose, instead of the one-size-fits-all book a store sells everyone.
- Will it read like generic AI content?
No. Your book isn't a chat transcript: it's planned chapter by chapter before a single word is written, told in a clear book voice, and explains ideas visually with charts, tables, and diagrams. After writing, every book goes through an editorial pass that polishes chapters so the book reads consistent from start to finish. Judge for yourself: browse thousands of sample books on our Explore Books page.
- How accurate is the content?
Our AI first checks whether your subject needs live research. Niche and fast-moving subjects are researched before writing, and the book plan and chapters are grounded in what it finds. After writing, every book goes through a quality pass that checks its facts and consistency, and researched books list their sources in a Notes section at the back.
- How long is the book?
You choose the length: Comprehensive (250-300 pages), Detailed (150-200 pages), Essential (70-100 pages), or Short (30-50 pages).
- Does the book include visuals?
Yes. Every book includes charts, tables, and diagrams: timelines, checklists, step-by-step guides, decision trees, comparison tables, matrices, and bar charts. A typical book includes dozens of these visual elements.
- Can I read it on Kindle? What formats can I download?
Yes. Every book can be read in our online reader or downloaded as a PDF or EPUB. The EPUB can be opened with Kindle, Apple Books, Kobo, and any e-reader. The Commercial and Author licenses also include an editable Word (DOCX) and Markdown download.
- How much does it cost?
About the price of a regular ebook. The exact price depends on your book's length and complexity, from $2 for the shortest books to $35 for the most comprehensive, and it's shown when you review your book, before you commit to anything. Each book is a one-time purchase, yours to keep, no subscription. Licenses that let you share, teach, or publish your book range from $35.99 to $49.99.
- Can I preview the book before purchasing?
Before you pay, you'll see what your book will cover: the title, a detailed description, the estimated length, and the complete chapter-by-chapter table of contents, so you know what you're getting before you decide. The full text itself is written after you purchase.
- How long does it take to create a book?
About 10 minutes. You can start reading the opening chapters while the rest is still being written.