JWT Tokens Mastery
Secure Authentication and Authorization for Modern Backend Systems
Master the complete lifecycle of JWT tokens in production backend systems.
207 pages9 chaptersJul 19, 2026Authentication
About this book
You'll move beyond basic token creation to understand the cryptographic foundations, security implications, and architectural patterns that separate robust implementations from vulnerable ones. This book covers token structure and validation, advanced security practices including key rotation and revocation strategies, integration with OAuth 2.0 and OpenID Connect, and real-world implementation patterns across different system architectures. Learn how to design authentication flows that scale horizontally, implement proper token expiration and refresh mechanisms, and defend against common JWT vulnerabilities. Whether you're building microservices, API gateways, or distributed systems, you'll gain the knowledge to make informed architectural decisions and implement JWT-based authentication that your team can maintain confidently in production environments.
Table of contents
- IntroductionWhy JWT Tokens Matter in Modern Backend Systems, From Session-Based to Stateless Authentication, What You'll Learn in This Book, Prerequisites and AssumptionsRead below
- Chapter 1: JWT Fundamentals and Token StructureWhat Is a JWT and How Does It Work?, Anatomy of a JWT: Header, Payload, and Signature, Base64URL Encoding and Token Composition, Understanding Claims: Standard and Custom
- Chapter 2: Cryptographic Foundations and SigningSigning Algorithms: HMAC, RSA, and ECDSA, Symmetric vs. Asymmetric Key Approaches, How Signature Verification Prevents Token Tampering, Choosing the Right Algorithm for Your System
- Chapter 3: Token Lifecycle ManagementGenerating and Issuing Tokens Securely, Token Expiration: Short-Lived vs. Long-Lived Tokens, Refresh Token Patterns and Implementation, Token Revocation and Blacklisting Mechanisms
- Chapter 4: Validation and AuthorizationComplete Token Validation Workflow, Verifying Claims and Custom Assertions, From Authentication to Authorization with JWT Claims, Implementing Scopes and Permission-Based Access Control
- Chapter 5: Security Vulnerabilities and Defense StrategiesAlgorithm Confusion Attacks and Prevention, Key Management Failures and Secure Key Storage, Preventing Token Leakage and Exposure, Common Implementation Pitfalls and How to Avoid Them
- Chapter 6: Key Rotation and Operational SecurityKey Rotation Strategies and Schedules, JWKS Endpoints and Key Discovery, Implementing Zero-Downtime Key Rotation, Monitoring, Auditing, and Compliance
- Chapter 7: Integration with OAuth 2.0 and OpenID ConnectOAuth 2.0 Fundamentals and Grant Types, OpenID Connect and Identity Layers, Using JWTs as Access and ID Tokens, Third-Party Authentication and Delegation
- Chapter 8: Architecture Patterns and ImplementationJWT in Monolithic Applications, JWT in Microservices and Distributed Systems, API Gateway Patterns and Token Validation, Service-to-Service Authentication with JWTs
- Chapter 9: Practical Implementation Across Languages and FrameworksJWT Libraries and Best Practices by Language, Integration with Popular Web Frameworks, Testing JWT Authentication and Authorization, Debugging and Troubleshooting JWT Issues
- ConclusionKey Takeaways and Recap, Next Steps in Your JWT Journey, Staying Current with Security Best Practices
- Glossary
- Further Reading and Resources
Introduction
Authentication is one of those problems that looks simple until you try to scale it. A single server with a session store works fine for thousands of users. Add a second server, a third, a load balancer, and suddenly every request needs to find its session data somewhere. That coordination cost compounds quickly. JSON Web Token, or JWT, emerged as a practical answer to this problem: encode the authentication state directly into a signed token, hand it to the client, and let every server verify it independently without calling home to a central store.
The idea is elegant, and the adoption has been widespread. JWTs now appear in API authentication, mobile app backends, microservices communication, and identity federation across thousands of production systems. The specification itself, defined in RFC 7519, is compact enough to read in an afternoon. But the gap between reading the spec and building a secure, production-ready implementation is where most developers run into trouble. The format is simple; the security model is not.
Misconfigurations in JWT implementations have led to real security incidents. The algorithm confusion attack, where a server accepts a token signed with the wrong algorithm, has been exploited in the wild against libraries that trusted the algorithm field inside the token itself. Token leakage through browser storage, overly long expiration windows, and missing Audience validation are all common patterns that quietly undermine systems that otherwise look correct. Understanding why these failures happen, not just what to avoid, is what separates a developer who can follow a tutorial from one who can design a trustworthy system.
This book is built for that second kind of developer. It assumes you already know what HTTP is, have written backend code in at least one language, and have a working mental model of how authentication generally works. From that foundation, it builds outward: through token structure, cryptographic signing, lifecycle management, security vulnerabilities, key rotation, OAuth 2.0 and OpenID Connect integration, and architecture patterns for systems ranging from a single monolith to a distributed microservices mesh.
Why JWT Tokens Matter in Modern Backend Systems
Modern backend systems rarely run on a single machine. Horizontal scaling, containerized deployments, and geographically distributed infrastructure have become the default for any application expecting real traffic. In these environments, the classic server-side session model creates a coordination problem. If a user authenticates on server A, server B has no knowledge of that session unless both servers share a session store, typically a Redis cluster or a database. That shared store becomes a dependency that every service must reach on every authenticated request.
JWTs sidestep this dependency entirely. The token carries its own authentication state, cryptographically signed so that any server holding the right key can verify it without making a network call. A user authenticates once, receives a token, and that token is self-contained proof of identity for every subsequent request. This is what the term stateless authentication means in practice: the server holds no per-user state between requests. The token is the state.
This property has concrete operational benefits. Services can scale independently. New instances come online and immediately handle authenticated requests without synchronizing session data. Deployments become simpler because there is no session affinity requirement. In a microservices architecture, a single token issued by an identity service can be verified by a dozen downstream services, each independently, without any of them calling back to the issuer for every request.
JWTs also enable cross-domain and cross-service authentication patterns that session cookies cannot easily support. A token issued by one service can carry claims that authorize access to a completely different service, as long as both services trust the same signing key or the same issuer. This is the foundation of how OAuth 2.0 and OpenID Connect work at scale, and it is why JWTs became the default token format for modern identity protocols.
The tradeoffs are real, though. Statelessness means that revoking a token before it expires requires additional infrastructure, typically a token blacklist or a short expiration window combined with a refresh token pattern. The token is visible to anyone who intercepts it, so transport security and storage choices matter. And the flexibility of the format, which allows any claims to be embedded, creates surface area for misconfiguration. These tradeoffs are not reasons to avoid JWTs; they are reasons to understand them deeply before deploying them.
The practical reality is that JWTs are already in your stack, or they will be soon. Every major cloud provider's identity service issues them. Every popular OAuth 2.0 provider uses them. The question is not whether to use JWTs but how to use them correctly, and what to watch for when something goes wrong.
A JWT is not just a token format. It is a contract between the issuer and every service that accepts it. The strength of that contract depends entirely on how carefully it is implemented on both sides.
From Session-Based to Stateless Authentication
To understand what JWTs solve, it helps to be precise about what session-based authentication actually does. When a user logs in, the server creates a session record, stores it somewhere (memory, a database, a cache), and sends the client a session ID, usually as a cookie. On every subsequent request, the client sends that session ID back, and the server looks it up to find the associated user data. The session ID itself is meaningless without the server-side record it points to.
This lookup step is the core constraint. It works well on a single server. It works acceptably with a shared session store, though that store now becomes a single point of failure and a performance bottleneck under high load. It becomes genuinely painful in architectures where services are independently deployed and scaled, because every service either needs access to the shared store or needs to call an authentication service on every request. Both options add latency and coupling.
Stateless authentication flips this model. Instead of storing state on the server and giving the client a pointer to it, the server encodes the state directly into a token and gives the client the state itself. The token contains the user's identity, roles, permissions, and expiration time. The server verifies the token's signature to confirm it was issued legitimately, then reads the claims directly from the token. No lookup required.
The shift has practical consequences that go beyond performance. Consider a concrete example: a user logs into a web application that is backed by three microservices, an order service, an inventory service, and a payment service. With session-based auth, each service either shares a session store or delegates every auth check to a central service. With JWT-based auth, the user's token is verified locally by each service using a shared public key or a shared secret. The services are decoupled from the authentication infrastructure at runtime.
The tradeoff that comes with this model is worth stating plainly. A session can be invalidated instantly by deleting the server-side record. A JWT cannot be "un-issued" once it leaves the server. If a token is stolen or a user's permissions change, the token remains valid until it expires. This is why short-lived tokens combined with refresh token rotation are the standard pattern for production systems. The expiration window limits the damage window. The refresh mechanism keeps the user experience smooth without requiring long-lived tokens.
Neither model is universally superior. Session-based authentication is simpler to reason about for small, single-server applications where instant revocation matters more than scalability. Stateless JWT authentication is better suited to distributed systems, API-first architectures, and scenarios where multiple independent services need to verify identity without coordination. Knowing which model fits your system is the first architectural decision this book will help you make confidently.
One more distinction matters here. JWTs are often described as a replacement for sessions, but that framing is too narrow. JWTs are a token format, not an authentication protocol. They can carry session-like data, but they can also carry delegation grants, service-to-service credentials, and identity assertions from third-party providers. The format is flexible enough to serve all of these purposes, which is exactly why understanding the format precisely, rather than just copying examples, is so important.
What You'll Learn in This Book
This book is organized as a progression from fundamentals to production-grade implementation. Each chapter builds on the previous one, but each is also self-contained enough to serve as a reference when you need to revisit a specific topic. The goal is not to give you a recipe to copy but to give you a mental model that lets you reason about JWT problems you have not seen before.
The journey starts with the token itself. The chapter on JWT Fundamentals and Token Structure covers what a JWT actually is at the byte level: how the Header, Payload, and Signature are composed, what Base64URL encoding does and does not do, and what Standard claims like iss (Issuer), sub (Subject), aud (Audience), exp (Expiration Time), and jti (JWT ID) are actually for. This foundation matters because every security decision downstream depends on understanding what is in the token and what each field means.
From there, the book moves into cryptography. The chapter on Cryptographic Foundations and Signing explains how HMAC-SHA256, RSA-SHA256, and ECDSA work at a conceptual level, what the difference between Symmetric signing and Asymmetric signing means for your architecture, and how Signature verification actually prevents tampering. You do not need a mathematics background to follow this chapter, but you will come away understanding why algorithm choice is a security decision, not just a configuration detail.
The lifecycle chapter covers the operational side: Token issuance, Token expiration, the Refresh token pattern, Refresh token rotation, and Token revocation including Token blacklist approaches. This is where the theory meets the user experience, and where the tradeoffs between security and convenience become concrete.
Validation and authorization follow. The Token validation workflow chapter walks through every check that must happen when a token arrives at your service, including Issuer validation, Audience validation, expiration checks, and Signature verification. The authorization chapter covers how to translate JWT claims into access decisions, including Scope, Role claim, and Permission-based access control patterns.
Security vulnerabilities get their own dedicated chapter because the failure modes of JWT implementations are specific and well-documented. The Algorithm confusion attack, Key management failure, and Token leakage are not theoretical concerns. They have affected real systems. Understanding how each attack works is the most reliable way to build defenses that actually hold.
The remaining chapters cover operational security through Key rotation and JWKS endpoint management, integration with OAuth 2.0 and OpenID Connect, architecture patterns for monoliths, microservices, and API gateway token validation, and practical implementation using libraries like jsonwebtoken (Node.js), PyJWT, jjwt (Java), and golang-jwt. Each of these chapters is grounded in real implementation decisions, not just concepts.
Prerequisites and Assumptions
This book is written for intermediate backend developers and software architects. It does not start from zero on programming or web development. If you have built a REST API, handled HTTP requests and responses, and written server-side code in at least one language, you have the foundation this book builds on. The code examples span multiple languages, but the concepts are language-agnostic, so fluency in any one backend language is sufficient.
A working familiarity with authentication concepts is assumed. You should know what a login flow looks like, what a cookie is, and roughly how HTTPS protects data in transit. You do not need to have implemented JWT authentication before. You do not need a background in cryptography. The cryptographic concepts covered in this book are explained from first principles, with the goal of building intuition rather than mathematical rigor.
Some chapters assume familiarity with distributed systems concepts. Terms like load balancer, microservice, and API gateway are used without extensive definition. If these are new to you, a brief read on each concept before reaching those chapters will make the material more concrete. The architecture chapters in particular will be most useful to developers who have worked in or are designing systems with multiple independently deployed services.
Here is a quick checklist of what you should be comfortable with before starting:
- Writing and reading HTTP request/response structures, including headers and status codes
- Building or consuming REST APIs in at least one backend language
- Basic understanding of how cookies and browser storage work
- General awareness of what authentication and authorization mean as distinct concepts
- Comfort reading pseudocode or code examples in languages you may not primarily use
What you do not need to bring to this book:
- Prior experience implementing JWT authentication
- A cryptography background or knowledge of specific algorithms
- Experience with OAuth 2.0 or OpenID Connect (these are covered from the ground up)
- Familiarity with any specific framework or cloud provider
The book uses concrete code examples throughout, drawn from real libraries in Node.js, Python, Java, and Go. These examples are meant to illustrate concepts, not to serve as copy-paste production code. Every example should be read with the question "why is it written this way?" in mind, not just "what does it do?" That habit of questioning implementation choices is the most transferable skill this book can give you.
One assumption worth stating explicitly: this book treats security as a first-class concern throughout, not as an afterthought in a dedicated chapter. Security decisions appear in the token structure chapter, the lifecycle chapter, the validation chapter, and everywhere else they are relevant. The dedicated security chapter covers specific attack vectors in depth, but the security mindset runs through the entire book. That is intentional. In JWT implementations, the most dangerous mistakes are often made in the most ordinary-looking code.
By the time you finish this book, you should be able to design a JWT-based authentication system from scratch, evaluate the security of an existing implementation, make informed decisions about algorithm selection and key management, integrate JWTs with OAuth 2.0 and OpenID Connect providers, and debug token validation failures in production. Those are not abstract goals. Each chapter is structured to move you toward one or more of them in a concrete, measurable way.
This is the end of the free sample. The full book has 9 chapters.
Want this book written for you?
Tell us your goals and background, and get your own version of this book, tailored by AI to you.


Benefits of AI-tailored books
- Read one book, not ten:
- all the Authentication knowledge you need, gathered into a single book.
- Save days of learning:
- tell us your goals, choose your topics, and the whole book is built around them.
- Learn effortlessly:
- Authentication book written for your specific background and expertise.
- Understand at a glance:
- includes charts, tables, timelines, checklists, decision trees, and more.
- Stay current:
- written the day you order it, not years ago.
- Trust what you read:
- every book is checked for accuracy, with real research when your subject needs it.
Create your unique book in 3 steps
- 1. Select your focus
Select the focus of your Authentication book and share your background
- 2. Personalize your book
Specify your goals and choose sub-topics to include
- 3. Get your tailored book
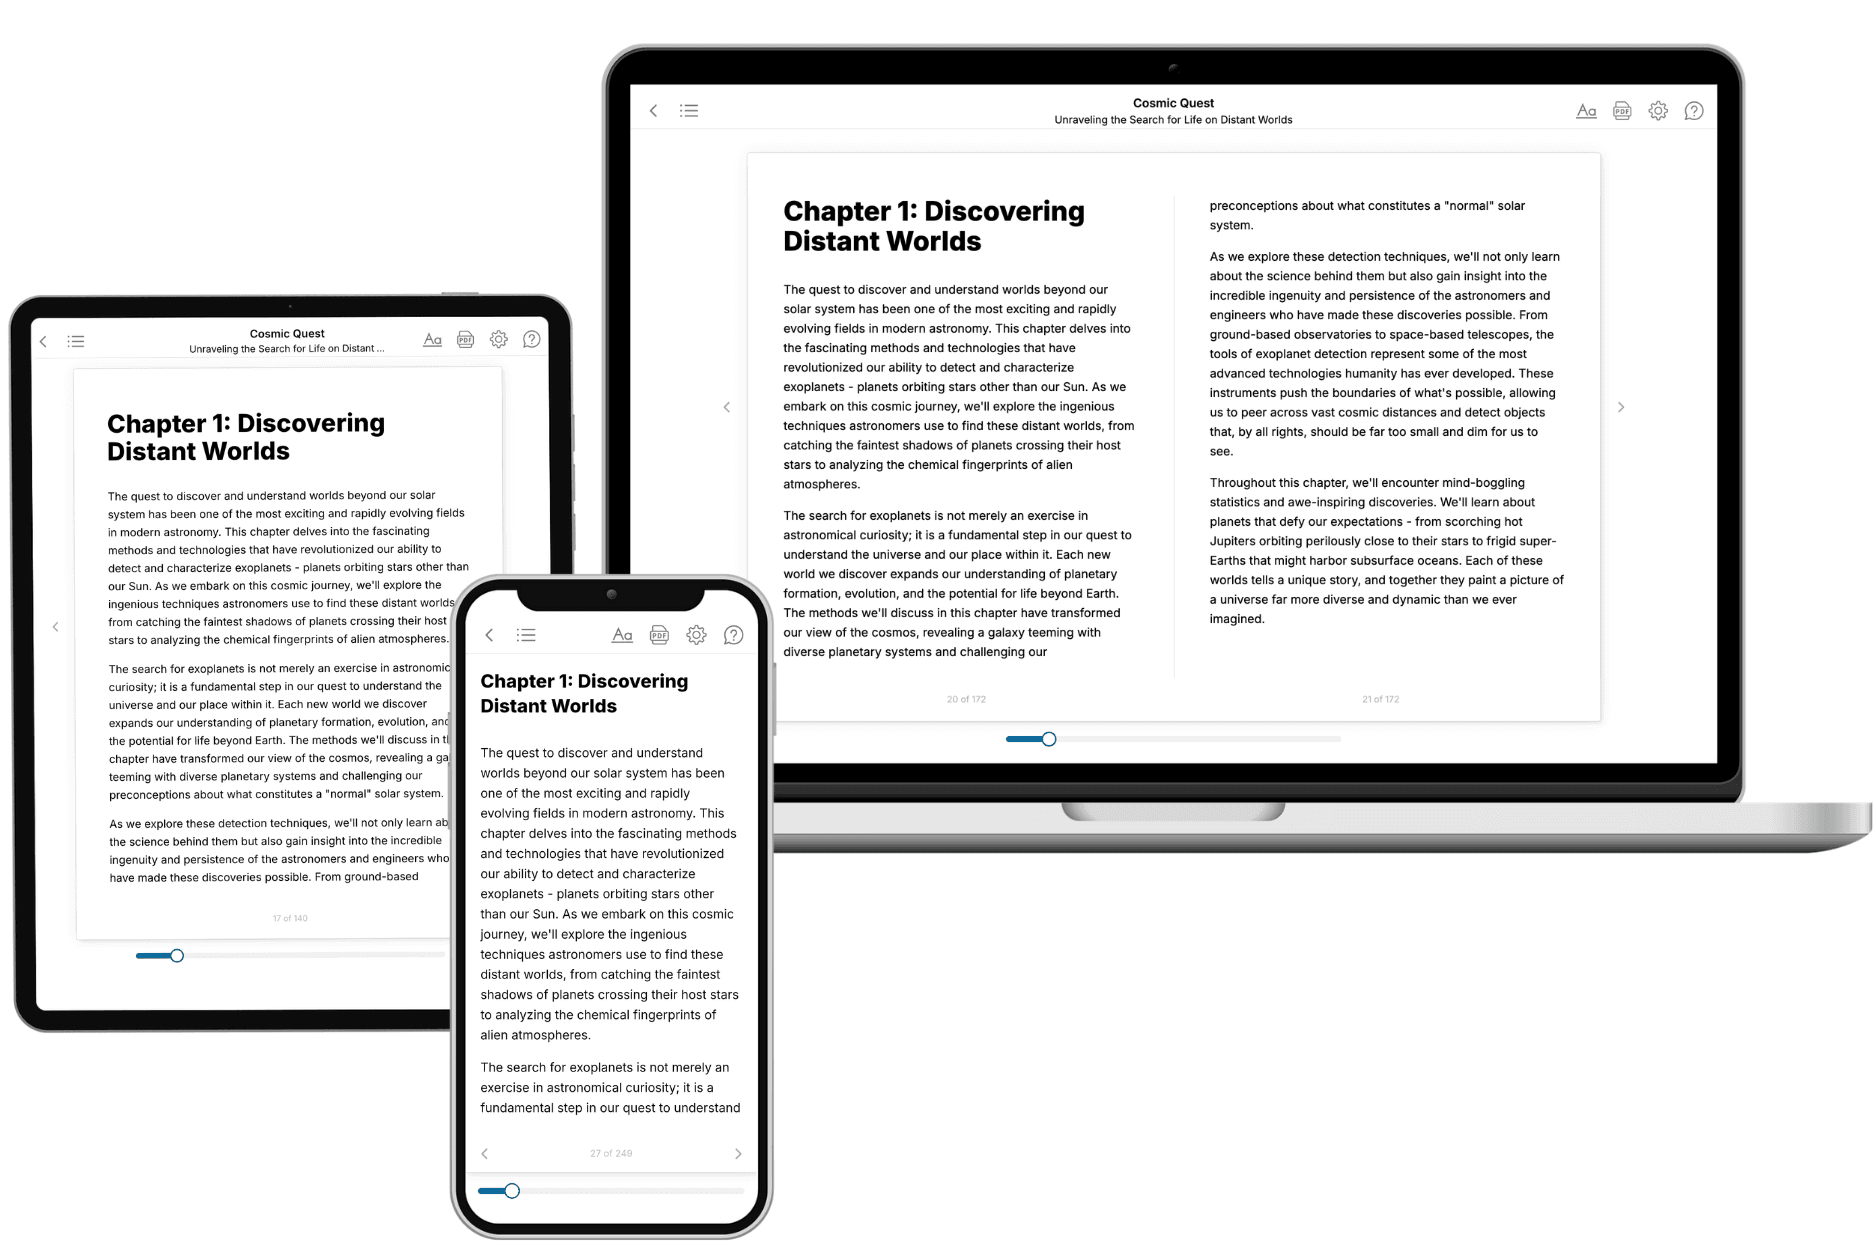
Your book is ready in 10 minutes. Read it online, download as EPUB or PDF, or send to Kindle.
Frequently asked questions
- What is TailoredRead?
TailoredRead creates complete, full-length nonfiction ebooks, written specifically for you. Tell us what you want to learn and why, and TailoredRead writes you a complete ebook on it, with charts, tables, and diagrams throughout. Read it online, on Kindle, or on any e-reader, or download it as a PDF or EPUB. Every book is written fresh the day you order it.
- How is the book tailored to me?
Before anything is written, you answer a few short questions about your goals, your background, and the topics you care about. Your book is then planned around your answers: written at your level, focused on your goals, and covering the topics you chose, instead of the one-size-fits-all book a store sells everyone.
- Will it read like generic AI content?
No. Your book isn't a chat transcript: it's planned chapter by chapter before a single word is written, told in a clear book voice, and explains ideas visually with charts, tables, and diagrams. After writing, every book goes through an editorial pass that polishes chapters so the book reads consistent from start to finish. Judge for yourself: browse thousands of sample books on our Explore Books page.
- How accurate is the content?
Our AI first checks whether your subject needs live research. Niche and fast-moving subjects are researched before writing, and the book plan and chapters are grounded in what it finds. After writing, every book goes through a quality pass that checks its facts and consistency, and researched books list their sources in a Notes section at the back.
- How long is the book?
You choose the length: Comprehensive (250-300 pages), Detailed (150-200 pages), Essential (70-100 pages), or Short (30-50 pages).
- Does the book include visuals?
Yes. Every book includes charts, tables, and diagrams: timelines, checklists, step-by-step guides, decision trees, comparison tables, matrices, and bar charts. A typical book includes dozens of these visual elements.
- Can I read it on Kindle? What formats can I download?
Yes. Every book can be read in our online reader or downloaded as a PDF or EPUB. The EPUB can be opened with Kindle, Apple Books, Kobo, and any e-reader. The Commercial and Author licenses also include an editable Word (DOCX) and Markdown download.
- How much does it cost?
About the price of a regular ebook. The exact price depends on your book's length and complexity, from $2 for the shortest books to $35 for the most comprehensive, and it's shown when you review your book, before you commit to anything. Each book is a one-time purchase, yours to keep, no subscription. Licenses that let you share, teach, or publish your book range from $35.99 to $49.99.
- Can I preview the book before purchasing?
Before you pay, you'll see what your book will cover: the title, a detailed description, the estimated length, and the complete chapter-by-chapter table of contents, so you know what you're getting before you decide. The full text itself is written after you purchase.
- How long does it take to create a book?
About 10 minutes. You can start reading the opening chapters while the rest is still being written.