SSH Mastery
Complete Guide to Secure Shell Protocols in Modern Network Infrastructure
Navigate the complexities of modern network security through comprehensive mastery of Secure Shell protocols.
300 pages16 chaptersOct 14, 2025Networking
About this book
This guide takes you from fundamental SSH concepts to advanced implementation strategies, providing the technical depth needed to secure enterprise networks effectively. You'll discover how SSH fits within the OSI model framework and learn to implement robust authentication mechanisms that protect against contemporary threats. Through practical examples and real-world scenarios, you'll master key management, tunneling techniques, and advanced configuration options that separate competent administrators from true SSH experts. The book progresses systematically through SSH architecture, cryptographic foundations, and practical deployment strategies. You'll gain expertise in troubleshooting common issues, optimizing performance, and implementing SSH in complex network environments. Each chapter builds upon previous concepts while introducing new techniques for leveraging SSH's full potential. By the final page, you'll possess the knowledge to design, implement, and maintain secure SSH infrastructures that meet enterprise-grade security requirements while supporting efficient remote administration workflows.
Table of contents
- IntroductionThe Evolution of Secure Shell, Modern Network Security Challenges, How This Book Approaches SSH Mastery, Prerequisites and ExpectationsRead below
- Chapter 1: SSH Fundamentals and ArchitectureProtocol Overview and Design Principles, SSH Within the OSI Model Framework, SSH-1 vs SSH-2: Critical Differences, Connection Establishment and Lifecycle
- Chapter 2: Cryptographic FoundationsSymmetric Encryption in SSH, Public Key Cryptography Essentials, Hash Functions and Message Authentication, Key Exchange Algorithms and Protocols
- Chapter 3: Authentication MechanismsPassword-Based Authentication, Public Key Authentication Methods, Host-Based Authentication Strategies, Multi-Factor Authentication Integration
- Chapter 4: SSH Key ManagementKey Generation Best Practices, Secure Key Distribution Methods, Key Rotation and Lifecycle Management, Secure Key Storage Solutions
- Chapter 5: SSH Client ConfigurationBasic Client Setup and Usage, Configuration Files and Options, Connection Multiplexing and Persistence, Client-Side Security Hardening
- Chapter 6: SSH Server ConfigurationServer Installation and Initial Setup, SSH Daemon Configuration Options, User and Group Access Controls, Server Security Hardening Techniques
- Chapter 7: Port Forwarding and TunnelingLocal Port Forwarding Techniques, Remote Port Forwarding Applications, Dynamic Port Forwarding and SOCKS Proxies, Tunnel Security and Best Practices
- Chapter 8: Secure File Transfer ProtocolsSCP Protocol and Usage, SFTP Protocol and Advanced Operations, Rsync over SSH for Synchronization, Transfer Performance Optimization
- Chapter 9: SSH Automation and ScriptingAutomated Connection Management, Batch Operations and Remote Execution, Configuration Management Integration, Monitoring and Alerting Automation
- Chapter 10: Network Integration and ArchitectureFirewall and Network Security Integration, SSH Load Balancing Strategies, VPN and SSH Coexistence, Network Segmentation with SSH
- Chapter 11: Performance OptimizationCipher Suite Selection and Performance, Compression Techniques and Trade-offs, Connection Parameter Tuning, Bandwidth Optimization Strategies
- Chapter 12: Troubleshooting and DiagnosticsCommon Connection Issues and Solutions, Debugging Techniques and Tools, Log Analysis and Interpretation, Network-Level Diagnostic Approaches
- Chapter 13: Advanced Security HardeningSSH Threat Modeling and Risk Assessment, Intrusion Detection and Prevention, Certificate Authority Integration, Security Standards and Compliance
- Chapter 14: Enterprise Deployment StrategiesScalability Planning and Architecture, Centralized SSH Management Solutions, Disaster Recovery and Business Continuity, Change Management and Documentation
- Chapter 15: Monitoring and LoggingComprehensive Logging Strategies, Monitoring Tools and Metrics, Alerting Systems and Incident Response, Audit Trails and Forensic Analysis
- Chapter 16: Emerging Technologies and Future TrendsQuantum-Resistant Cryptography Preparation, Container and Orchestration Integration, Cloud-Native SSH Implementations, Protocol Evolution and Standards Development
- Conclusion
- Glossary
Introduction
Network security has evolved dramatically since the early days of computing, yet one protocol has remained consistently relevant and increasingly critical: Secure Shell (SSH). In today's interconnected world, where remote work has become the norm and cloud infrastructure spans global networks, SSH serves as the backbone of secure system administration and remote access. This protocol, which began as a solution to the inherent insecurities of telnet and rlogin, has grown into a comprehensive suite of tools that enable secure communication across untrusted networks. Understanding SSH is no longer optional for network administrators and IT professionals—it's essential for maintaining the security and integrity of modern computing environments.
The complexity of contemporary network infrastructures demands more than superficial knowledge of SSH commands and basic configuration. Today's IT professionals must understand the cryptographic foundations that make SSH secure, the architectural decisions that affect performance and security, and the integration patterns that enable SSH to work effectively within broader security frameworks. This depth of understanding becomes crucial when designing systems that must withstand sophisticated attacks while maintaining the usability and performance that modern organizations require. The stakes are higher than ever, with data breaches and security incidents making headlines regularly, often stemming from inadequate remote access controls or misconfigured secure communication channels.
This book addresses the gap between basic SSH usage and true mastery of the protocol. While many resources cover the fundamentals of connecting to remote systems, few provide the comprehensive understanding needed to implement SSH securely at enterprise scale. You'll discover not just how to use SSH, but why it works the way it does, how to optimize it for different scenarios, and how to integrate it seamlessly into complex network architectures. The journey from basic user to SSH expert requires understanding the protocol's place within the OSI model, mastering its cryptographic underpinnings, and developing the practical skills needed to troubleshoot issues and optimize performance in real-world environments.
The Evolution of Secure Shell
The story of SSH begins in 1995 when Tatu Ylönen, a researcher at Helsinki University of Technology, witnessed a password-sniffing attack on his university's network. This incident highlighted the fundamental security flaws in the remote access protocols of the time, particularly telnet, rlogin, and rsh, which transmitted all data, including passwords, in plain text across networks. Ylönen's response was to create the first version of SSH, which he released as free software to address these critical security vulnerabilities. The initial SSH-1 protocol introduced revolutionary concepts for its time: strong encryption of all communication, secure authentication mechanisms, and protection against various network-based attacks that plagued earlier protocols.
The transition from SSH-1 to SSH-2 marked a significant evolution in the protocol's design and security model. Released in 2006 as RFC 4251-4254, SSH-2 addressed several critical vulnerabilities discovered in the original protocol and introduced substantial improvements in both security and functionality. The new version implemented a more robust key exchange mechanism, better encryption algorithms, and improved message authentication codes. Perhaps most importantly, SSH-2 introduced a modular architecture that allowed for easier extension and customization, enabling the protocol to adapt to evolving security requirements and cryptographic advances. This architectural flexibility has proven crucial as SSH has evolved to meet the demands of modern computing environments.
Throughout its evolution, SSH has consistently stayed ahead of emerging security threats while maintaining backward compatibility where possible. The protocol has adapted to incorporate new cryptographic algorithms as they've been developed and standardized, ensuring that SSH implementations can leverage the latest advances in cryptographic research. For example, modern SSH implementations support elliptic curve cryptography, which provides equivalent security to traditional RSA keys with significantly smaller key sizes, improving both performance and security. The protocol has also evolved to support new authentication methods, including integration with modern identity management systems and multi-factor authentication mechanisms.
The widespread adoption of SSH across different platforms and operating systems has created a rich ecosystem of implementations and tools. From the original SSH implementation to modern variants like OpenSSH, which has become the de facto standard on Unix-like systems, the protocol has been ported to virtually every computing platform. This ubiquity has made SSH the universal language of secure remote access, enabling administrators to manage diverse infrastructure using consistent tools and techniques. The protocol's success has also led to its integration into numerous other tools and systems, from version control systems like Git to configuration management platforms and cloud orchestration tools.
Modern SSH implementations continue to evolve in response to contemporary challenges such as quantum computing threats, containerized environments, and cloud-native architectures. Recent developments include support for post-quantum cryptographic algorithms, improved integration with certificate authorities for large-scale key management, and enhanced logging and auditing capabilities to meet compliance requirements. The protocol's ability to adapt while maintaining its core security principles demonstrates the soundness of its original design and ensures its continued relevance in an ever-changing technological landscape.
Understanding this evolutionary history provides crucial context for modern SSH deployment decisions. The lessons learned from early security vulnerabilities inform current best practices, while the protocol's demonstrated adaptability gives confidence in its future viability. As you progress through this book, you'll see how historical design decisions continue to influence modern SSH implementations and how understanding the protocol's evolution can guide your own deployment and configuration choices. This historical perspective also helps explain why certain configuration options exist and why some practices that might seem overly cautious are actually essential for maintaining security in hostile network environments.
Modern Network Security Challenges
Today's network security landscape presents unprecedented challenges that make robust SSH implementation more critical than ever. The proliferation of cloud computing has fundamentally changed how organizations approach infrastructure, with resources distributed across multiple cloud providers, hybrid environments, and edge locations. This distributed architecture creates complex security boundaries where traditional perimeter-based security models prove inadequate. SSH often serves as the primary mechanism for secure access to these distributed resources, making its proper implementation a cornerstone of modern security strategies. The challenge lies not just in securing individual SSH connections, but in managing SSH access across dynamic, scalable infrastructure where resources may be created and destroyed automatically based on demand.
The rise of sophisticated attack vectors has elevated the importance of understanding SSH's security mechanisms in depth. Advanced Persistent Threats (APTs) often target SSH infrastructure as a means of establishing persistent access to compromised networks. These attacks may involve compromised SSH keys, man-in-the-middle attacks against poorly configured clients, or exploitation of weak authentication mechanisms. Modern attackers understand SSH well enough to abuse its features, such as using SSH tunneling to exfiltrate data or establish covert communication channels. Defending against these threats requires more than basic SSH knowledge—it demands understanding of the protocol's cryptographic foundations, proper key management practices, and the ability to detect and respond to suspicious SSH activity.
Compliance requirements have added another layer of complexity to SSH deployment in enterprise environments. Regulations such as SOX, HIPAA, PCI DSS, and GDPR impose specific requirements for access controls, audit trails, and data protection that directly impact how SSH must be configured and monitored. These requirements often mandate specific cryptographic standards, key rotation schedules, and logging practices that go beyond basic security considerations. Organizations must balance security requirements with operational efficiency, ensuring that SSH implementations meet compliance standards without creating barriers to legitimate administrative activities. This balance requires deep understanding of both the technical capabilities of SSH and the specific requirements of applicable regulatory frameworks.
The scale of modern infrastructure presents unique challenges for SSH key management and access control. Large organizations may have thousands of servers and hundreds of administrators, creating a complex web of access relationships that must be managed securely and efficiently. Traditional approaches to SSH key management, such as manually distributing public keys to authorized_keys files, become unmanageable at scale and create security risks through inconsistent application of access policies. Modern SSH deployments must integrate with centralized identity management systems, support automated key rotation, and provide granular access controls that can be applied consistently across large, dynamic infrastructure. The challenge is compounded by the need to maintain access during system failures while preventing unauthorized access through compromised credentials.
Container orchestration and microservices architectures have introduced new paradigms that challenge traditional SSH deployment models. In containerized environments, the concept of long-lived servers with persistent SSH access gives way to ephemeral containers that may exist for only minutes or hours. This shift requires rethinking fundamental assumptions about SSH key distribution, host key verification, and access logging. Additionally, the service mesh architectures common in microservices deployments often provide their own secure communication mechanisms, raising questions about when and how SSH should be used in these environments. Understanding how SSH fits into modern application architectures requires knowledge of both traditional SSH deployment patterns and emerging cloud-native security models.
The increasing sophistication of network monitoring and traffic analysis capabilities has created both opportunities and challenges for SSH deployment. While improved monitoring tools enable better detection of suspicious SSH activity, they also require careful configuration to avoid overwhelming security teams with false positives. Modern SSH implementations must balance security with observability, providing sufficient logging and monitoring capabilities to detect threats while protecting sensitive information from unauthorized disclosure. This balance is particularly challenging in environments where SSH is used for automated processes, where the volume of connections may be high and the patterns of legitimate use may be difficult to distinguish from malicious activity.
Zero-trust security models have fundamentally changed how organizations approach network security, with implications for SSH deployment and configuration. In zero-trust environments, no connection is trusted by default, regardless of its source or destination. This approach requires SSH implementations that can integrate with dynamic authentication and authorization systems, support fine-grained access controls, and provide detailed audit trails for all activities. The challenge lies in implementing these capabilities without compromising the performance and usability that make SSH an effective tool for system administration. Understanding how to configure SSH for zero-trust environments requires knowledge of advanced authentication mechanisms, integration with identity providers, and the ability to implement and maintain complex access control policies.
How This Book Approaches SSH Mastery
This book takes a systematic approach to SSH mastery that builds from fundamental concepts to advanced implementation strategies. Rather than simply cataloging SSH commands and configuration options, the content is structured to develop deep understanding of the underlying principles that govern SSH behavior. Each chapter builds upon previous concepts while introducing new layers of complexity, ensuring that you develop both theoretical knowledge and practical skills. The approach emphasizes understanding the why behind SSH design decisions, enabling you to make informed choices when configuring SSH for specific environments and requirements. This foundation-first approach ensures that you can adapt your knowledge to new situations and technologies as they emerge.
The book integrates theoretical concepts with practical, real-world examples throughout each chapter. Rather than presenting abstract concepts in isolation, you'll encounter specific scenarios that demonstrate how SSH principles apply in actual network environments. These examples include detailed configuration snippets, step-by-step implementation guides, and troubleshooting scenarios based on common issues encountered in production environments. The practical examples are designed to be immediately applicable, allowing you to implement and test concepts as you learn them. This hands-on approach reinforces theoretical understanding while building the practical skills needed for effective SSH deployment and management.
A key differentiator of this book's approach is its emphasis on SSH's role within broader network architectures and security frameworks. Rather than treating SSH as an isolated protocol, the content consistently explores how SSH integrates with other network services, security tools, and infrastructure components. You'll learn how SSH fits within the OSI model, how it interacts with firewalls and intrusion detection systems, and how it can be leveraged as part of comprehensive security strategies. This systems-thinking approach prepares you to make architectural decisions that consider SSH's impact on overall network security and performance.
The book addresses the full lifecycle of SSH implementation, from initial planning and design through deployment, monitoring, and maintenance. This comprehensive coverage ensures that you understand not just how to configure SSH, but how to plan SSH deployments that will remain secure and manageable over time. Topics include capacity planning, key management strategies, monitoring and alerting approaches, and procedures for responding to security incidents. This lifecycle perspective is essential for enterprise environments where SSH infrastructure must be maintained and evolved over years or decades.
Throughout the book, special attention is paid to common pitfalls and misconceptions that can lead to security vulnerabilities or operational issues. Each major topic includes discussion of what can go wrong and how to avoid or remediate problems. These cautionary examples are drawn from real-world incidents and common misconfigurations observed in production environments. By understanding these failure modes, you'll be better equipped to design robust SSH implementations and troubleshoot issues when they arise. This defensive approach to learning helps build the judgment needed to make sound decisions under pressure.
The content is structured to support both sequential reading and reference use. While the chapters build upon each other logically, each section is designed to be self-contained enough to serve as a reference for specific topics. Cross-references throughout the text help you navigate between related concepts, and detailed examples provide templates that can be adapted for your specific needs. This dual-purpose design makes the book valuable both as a learning resource and as an ongoing reference for SSH implementation and troubleshooting.
Advanced topics are introduced gradually, with clear explanations of prerequisites and dependencies. Rather than assuming extensive background knowledge, the book provides sufficient context for each advanced concept while maintaining focus on practical application. This approach makes advanced SSH techniques accessible to readers with varying levels of experience while ensuring that the content remains valuable for seasoned professionals. The progressive complexity allows you to engage with the material at your current level while providing a clear path for developing more advanced skills.
Prerequisites and Expectations
This book assumes you have intermediate-level experience with network administration and system administration concepts. You should be comfortable working with command-line interfaces on Unix-like systems and have basic familiarity with network protocols and services. While the book explains SSH-specific concepts in detail, it builds upon foundational knowledge of TCP/IP networking, basic cryptographic concepts, and general system administration practices. If you're currently managing servers or network infrastructure in a professional capacity, you likely have the background knowledge needed to benefit from this content. The book does not assume prior SSH expertise, but it does expect familiarity with the types of problems that SSH is designed to solve.
A solid understanding of basic networking concepts is essential for getting the most from this book. You should understand how TCP connections are established and maintained, be familiar with concepts like ports and firewalls, and have experience troubleshooting network connectivity issues. Knowledge of the OSI model is helpful but not required, as the book explains SSH's place within this framework. Additionally, familiarity with basic security concepts such as encryption, authentication, and authorization will help you understand the security mechanisms that SSH employs. If you're uncertain about any of these prerequisites, consider reviewing basic networking and security resources before diving into the more advanced SSH concepts covered in later chapters.
From a practical standpoint, you'll get the most value from this book if you have access to systems where you can practice SSH configuration and testing. This might include virtual machines, cloud instances, or physical servers in a lab environment. Many of the examples and exercises in the book are designed to be tested in practice, and hands-on experience is crucial for developing true SSH mastery. You don't need expensive equipment or complex lab setups—simple virtual machines or cloud instances are sufficient for most of the concepts covered. The ability to experiment safely with different configurations will significantly enhance your learning experience.
The book expects readers to be comfortable with text-based configuration files and command-line tools. SSH configuration involves editing various text files, running command-line utilities, and interpreting log files and error messages. While the book provides detailed examples of all necessary commands and configurations, you should be comfortable navigating file systems, editing files with text editors, and interpreting command output. Experience with shell scripting is helpful for the automation chapters but is not strictly required, as the book provides sufficient context for the scripting examples presented.
Professional context is important for understanding the enterprise-focused aspects of this book. Many of the advanced topics, such as key management at scale, compliance requirements, and integration with enterprise identity systems, are most relevant to readers working in organizational environments with multiple systems and users. While the technical concepts apply universally, the practical examples and use cases assume you're dealing with the types of challenges that arise when managing SSH access for multiple users across multiple systems. Solo practitioners and small-scale deployments will still benefit from understanding these concepts, as they provide insight into SSH's full capabilities and prepare you for larger-scale implementations.
The book assumes you're working primarily with OpenSSH, which is the most widely deployed SSH implementation and the default on most Unix-like systems. While the fundamental concepts apply to other SSH implementations, specific configuration examples and command syntax are based on OpenSSH. If you're working with other SSH implementations, you may need to adapt some examples to match your specific software. The book notes significant differences between implementations where relevant, but the primary focus remains on OpenSSH due to its ubiquity and feature completeness.
Finally, this book expects readers who are committed to developing deep expertise rather than seeking quick fixes or superficial knowledge. SSH mastery requires understanding complex interactions between cryptographic protocols, network configurations, and system security policies. The book provides the depth needed for true expertise, but this comes with the expectation that you're willing to invest the time and effort needed to understand these complex topics thoroughly. If you're looking for a quick reference or basic tutorial, this book may be more comprehensive than you need. However, if you're committed to becoming an SSH expert who can design, implement, and troubleshoot complex SSH deployments, this book provides the comprehensive foundation you need.
This is the end of the free sample. The full book has 16 chapters.
Want this book written for you?
Tell us your goals and background, and get your own version of this book, tailored by AI to you.


Benefits of AI-tailored books
- Read one book, not ten:
- all the Networking knowledge you need, gathered into a single book.
- Save days of learning:
- tell us your goals, choose your topics, and the whole book is built around them.
- Learn effortlessly:
- Networking book written for your specific background and expertise.
- Understand at a glance:
- includes charts, tables, timelines, checklists, decision trees, and more.
- Stay current:
- written the day you order it, not years ago.
- Trust what you read:
- every book is checked for accuracy, with real research when your subject needs it.
Create your unique book in 3 steps
- 1. Select your focus
Select the focus of your Networking book and share your background
- 2. Personalize your book
Specify your goals and choose sub-topics to include
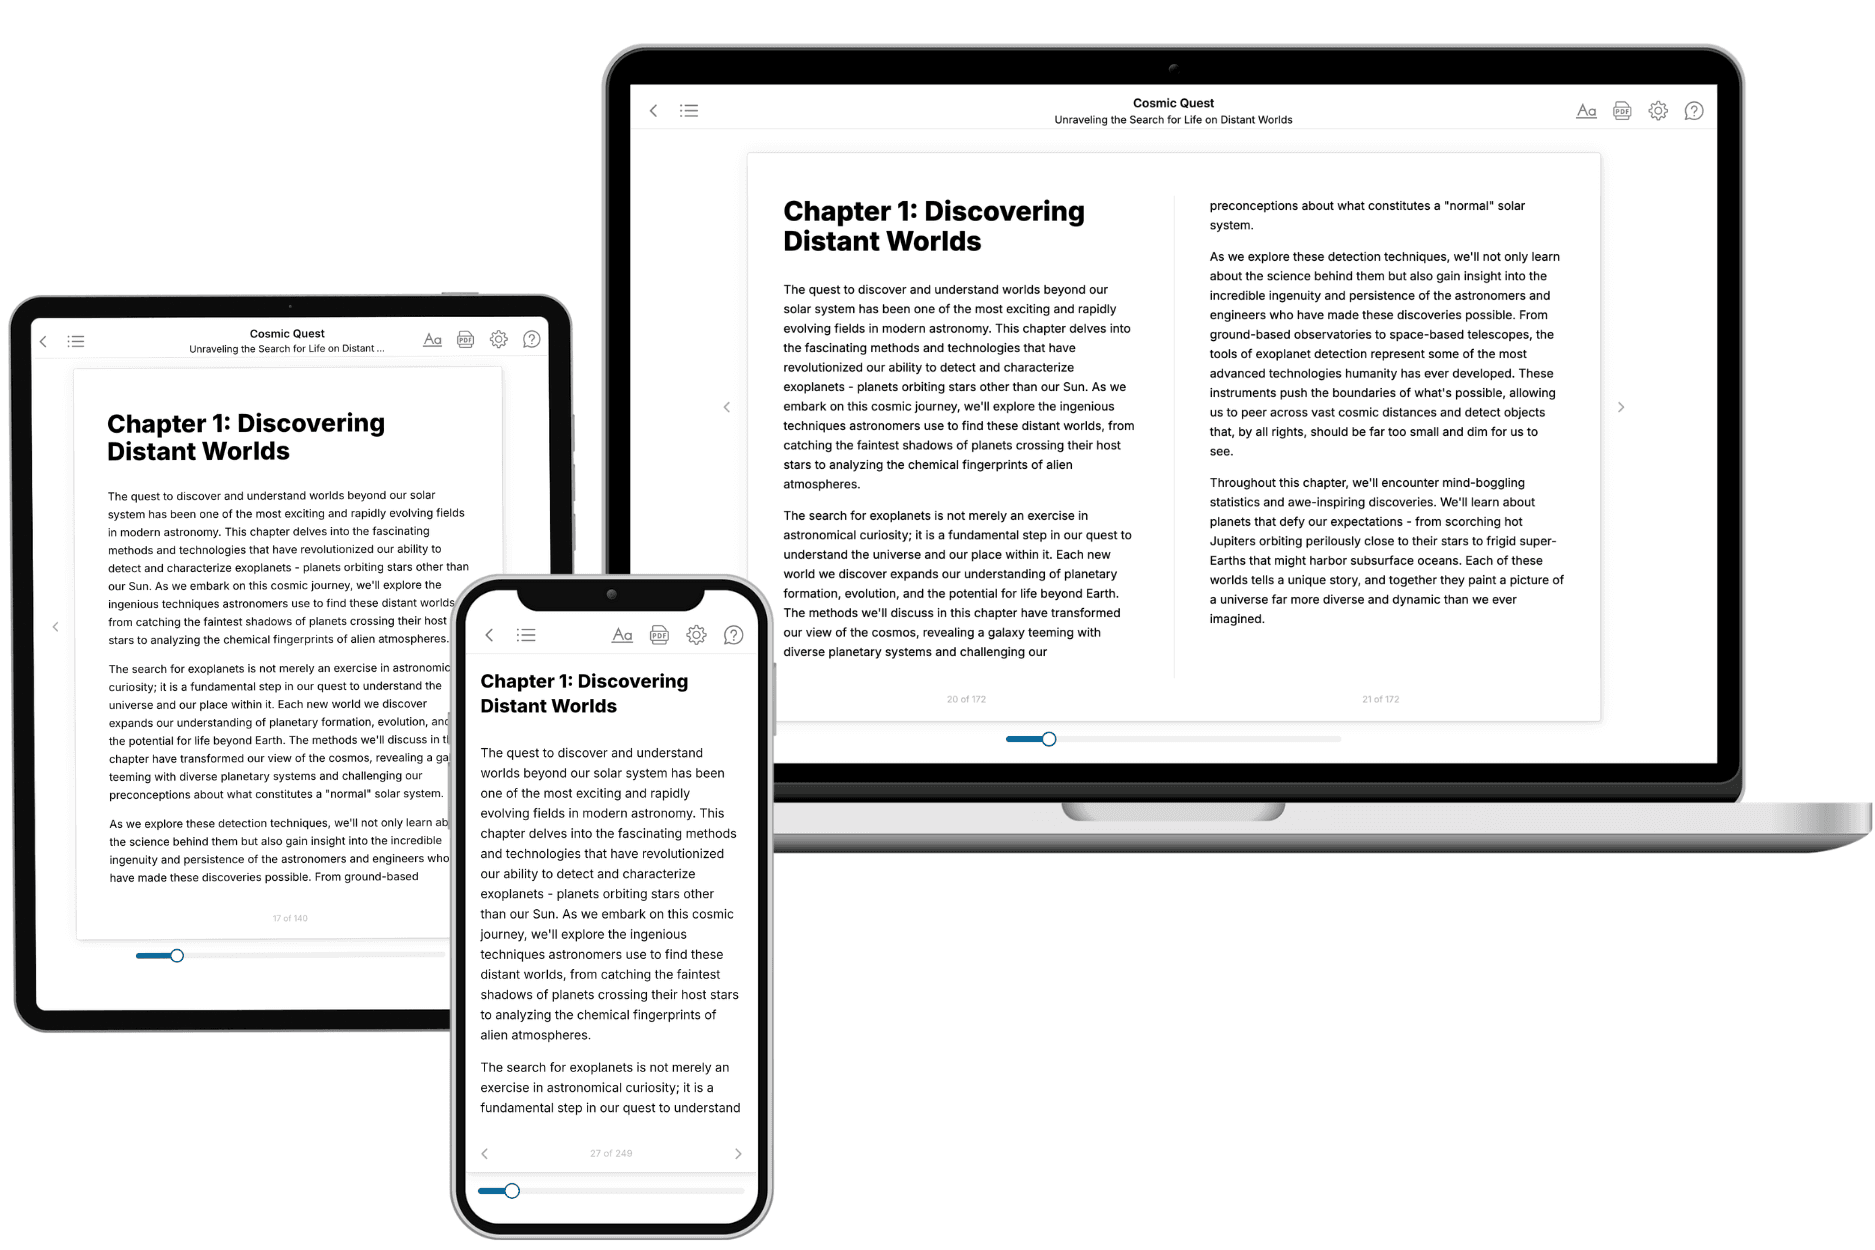
- 3. Get your tailored book
Your book is ready in 10 minutes. Read it online, download as EPUB or PDF, or send to Kindle.
Frequently asked questions
- What is TailoredRead?
TailoredRead creates complete, full-length nonfiction ebooks, written specifically for you. Tell us what you want to learn and why, and TailoredRead writes you a complete ebook on it, with charts, tables, and diagrams throughout. Read it online, on Kindle, or on any e-reader, or download it as a PDF or EPUB. Every book is written fresh the day you order it.
- How is the book tailored to me?
Before anything is written, you answer a few short questions about your goals, your background, and the topics you care about. Your book is then planned around your answers: written at your level, focused on your goals, and covering the topics you chose, instead of the one-size-fits-all book a store sells everyone.
- Will it read like generic AI content?
No. Your book isn't a chat transcript: it's planned chapter by chapter before a single word is written, told in a clear book voice, and explains ideas visually with charts, tables, and diagrams. After writing, every book goes through an editorial pass that polishes chapters so the book reads consistent from start to finish. Judge for yourself: browse thousands of sample books on our Explore Books page.
- How accurate is the content?
Our AI first checks whether your subject needs live research. Niche and fast-moving subjects are researched before writing, and the book plan and chapters are grounded in what it finds. After writing, every book goes through a quality pass that checks its facts and consistency, and researched books list their sources in a Notes section at the back.
- How long is the book?
You choose the length: Comprehensive (250-300 pages), Detailed (150-200 pages), Essential (70-100 pages), or Short (30-50 pages).
- Does the book include visuals?
Yes. Every book includes charts, tables, and diagrams: timelines, checklists, step-by-step guides, decision trees, comparison tables, matrices, and bar charts. A typical book includes dozens of these visual elements.
- Can I read it on Kindle? What formats can I download?
Yes. Every book can be read in our online reader or downloaded as a PDF or EPUB. The EPUB can be opened with Kindle, Apple Books, Kobo, and any e-reader. The Commercial and Author licenses also include an editable Word (DOCX) and Markdown download.
- How much does it cost?
About the price of a regular ebook. The exact price depends on your book's length and complexity, from $2 for the shortest books to $35 for the most comprehensive, and it's shown when you review your book, before you commit to anything. Each book is a one-time purchase, yours to keep, no subscription. Licenses that let you share, teach, or publish your book range from $35.99 to $49.99.
- Can I preview the book before purchasing?
Before you pay, you'll see what your book will cover: the title, a detailed description, the estimated length, and the complete chapter-by-chapter table of contents, so you know what you're getting before you decide. The full text itself is written after you purchase.
- How long does it take to create a book?
About 10 minutes. You can start reading the opening chapters while the rest is still being written.